

Endor Labs ✓
AI-powered application security that prioritizes real risks.
Verdict
A quick read before you dig into the full page.
- Best if
- AI-powered application security that prioritizes real risks
- Skip if
- Dependency on custom rules
- Pick this when
- Prioritizes real risks
Considering ZeroPath instead? Compare side by side
Overview
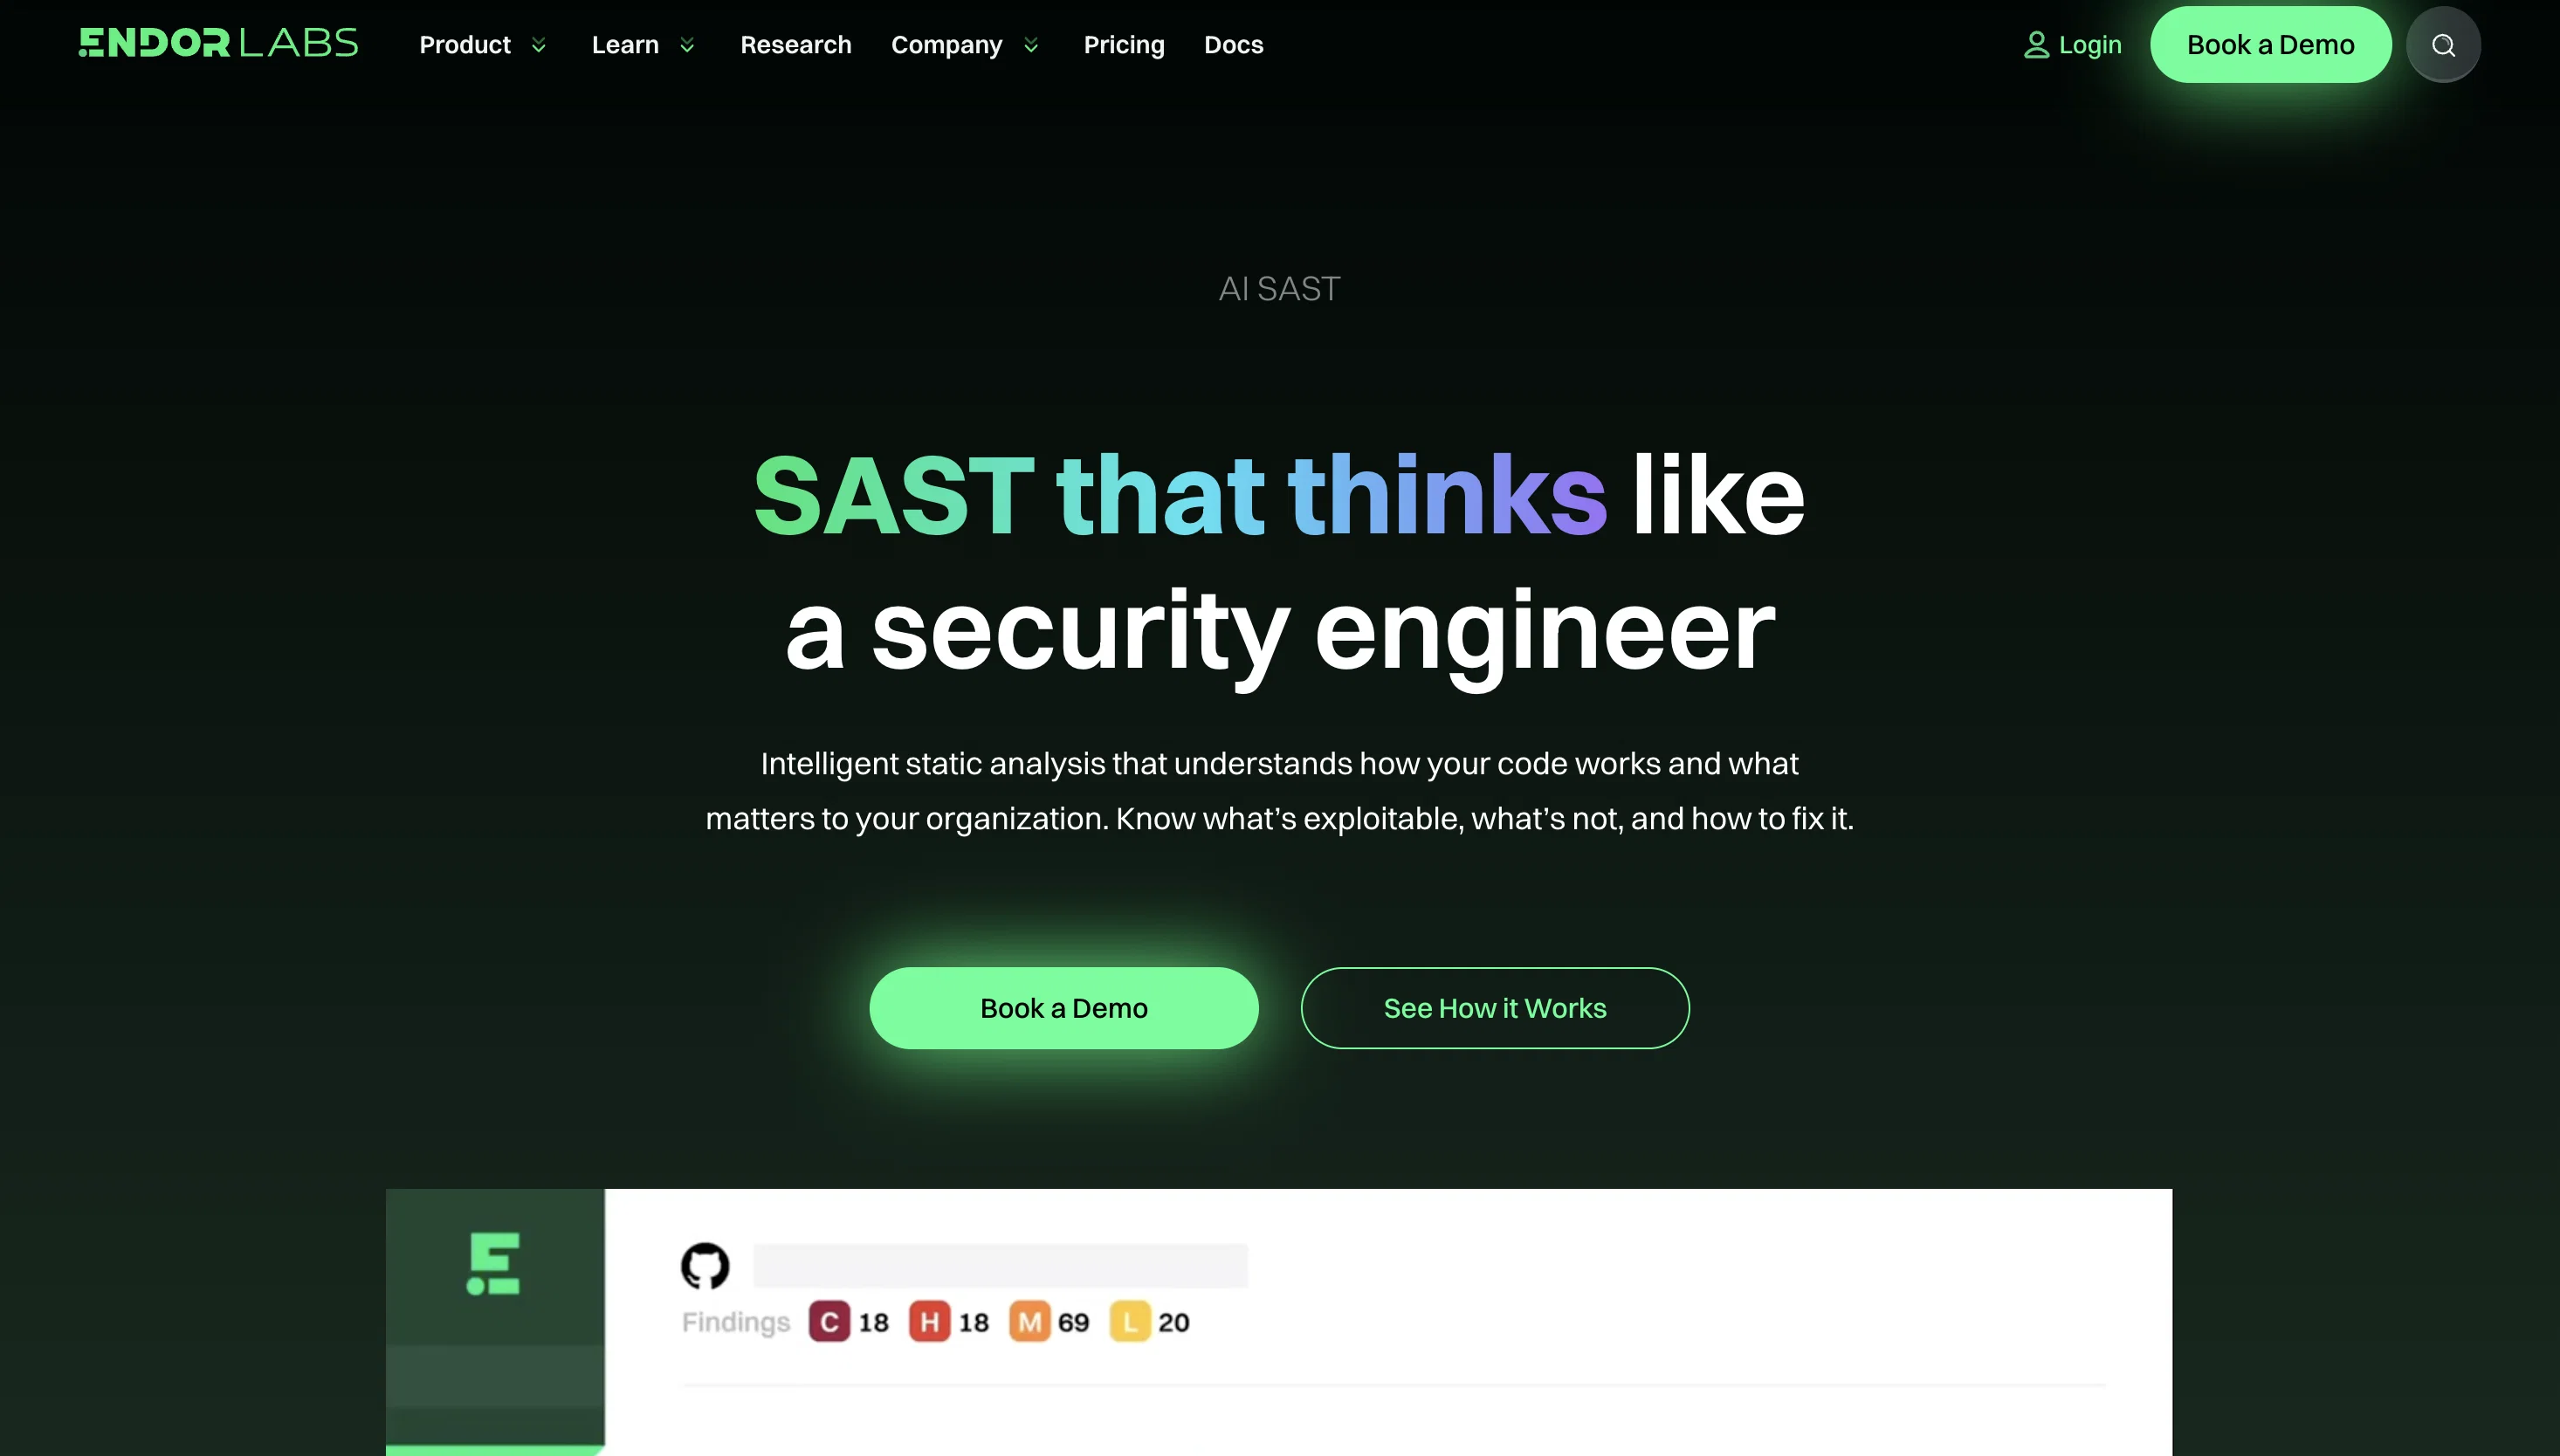
AURI is an AI static application security testing (SAST) tool developed by Endor Labs. Acting as security intelligence for AI coding agents, AURI helps teams prioritize real risks, reduce noise and remediate vulnerabilities quickly.
It understands how code works and identifies what matters most to the organisation. The tool intelligently analyses code, triaging false positives and validating multi-file and multi-function data flows.
It assists in identifying complex vulnerabilities beyond traditional rule-based scanning, such as business logic and authentication flaws. AURI integrates directly into AI code editors to give developers and agents the tools to fix code before their first commit.
The software automatically triages findings by parsing syntax, tracing data flow, and reasoning about context and logic to present issues that genuinely matter.
It validates findings, providing transparent evidence and reasoning for every decision. The tool allows the addition of custom prompts and rules to align agent behaviour with an organization's security policies, priorities, and threat models.
Moreover, AURI can highlight complex logic flaws and other risks typically found in pentest reports and bug bounty programs without the need for rule creation or upkeep.
It provides reachable findings and delivers precise, explainable fixes for developers. Additionally, AURI offers smart fix suggestions that generate context-aware solutions aligned with your codebase for review.
It supports over 40 languages, including Java, Javascript, Python, C#, C/C++, Go, Kotlin, TypeScript, Ruby, Rust, JSX, PHP, Scala, Swift, Terraform, and more.
Access & connections
Where you can use Endor Labs.
Platforms
Capabilities
What this tool accepts, produces, and is strongest at.
Input
- Code
Output
- Code
Pros & cons
Pros
- Prioritizes real risks
- Reduces noise
- Fast vulnerability remediation
- Identifies organizational importance
- Analyses multi-file data flows
- Triages false positives
- Detects complex vulnerabilities
- Syntax parsing
Show 39 more
- Data flow tracing
- Logical reasoning capacity
- Transparent evidence provision
- Custom rules addition
- Security policy alignment
- Threat modeling
- Identifies logical flaws
- Pentest report analysis
- Bug bounty compatibility
- Intelligent fix suggestions
- Supports 40+ languages
- Generates context-aware solutions
- Reachable findings
- Delivers precise fixes
- Explainable fixes
- Customization of prompts
- Vulnerability detection before commit
- Manual research skipping
- Auto-triage of findings
- Scalable coverage for risks
- Detects risky changes early
- LLM security issue identification
- High-signal finding focus
- Guides on remediation
- Verifiable trusted changes
- Monitor severity and risk
- Multi-file, multi-function analysis
- Authentication guard understanding
- Framework-specific sanitization
- Reduced false positives
- Add custom prompts
- Java, Javascript, Python support
- C#, C/C++, Go support
- Kotlin, TypeScript, Ruby support
- Rust, JSX, PHP support
- Scala, Swift, Terraform support
- Business logic flaws detection
- Authentication flaws detection
- Contextual analysis
Cons
- Dependency on custom rules
- No explicit mention of real-time support
- No explicit mobile language support
- No explicit built-in threat intelligence
- No explicit support for older languages
- May miss risks during auto-triage
- No explicit hardware security integration
- Dependent on code syntax parsing
Compare alternatives
Similar tools in the catalog — with a clear reason to open each one.

ZeroPath ✓
FreemiumAI-native SAST finding 2x more vulnerabilities with fewer false positives.
Why look Higher community rating
Full comparison
DryRun Security ✓
UnknownSecurity context as you code, without being a security expert.
No pricing
Full comparison
Releases 1
FAQ 12
What is Endor Labs AURI?
How does AURI prioritize real risks?
Can AURI validate multi-file and multi-function data flows?
How does AURI reduce noise in the code?
How does AURI understand how the code works?
How does AURI remediate vulnerabilities quickly?
What type of vulnerabilities can AURI identify?
How does AURI integrate with AI code editors?
How does AURI validate its findings?
Can we add custom prompts and rules in AURI?
Can AURI align with an organization's security policies and threat models?
Does AURI provide fix suggestions?
Related tools
Recommended

MailSweeper ✓
PaidReclaim your inbox with AI-powered email cleanup.
Invent | AI Customer Support Agents for any channel ✓
Free TrialYour AI business agent platform, on any channel

Voibe ✓
Free TrialType 3x faster with private offline dictation.

TheLibrarian.io ✓
Free TrialYour WhatsApp AI assistant for instant productivity.
Oddsmyth ✓
FreemiumYour AI co-manager for fantasy baseball.
devlo ✓
Free TrialAI Software Platform