

DryRun Security ✓
Security context as you code, without being a security expert.
Verdict
A quick read before you dig into the full page.
- Best if
- Security context as you code, without being a security expert
- Skip if
- Limited customization options
- Pick this when
- Automated in-line security checks
Considering ZeroPath instead? Compare side by side
Overview
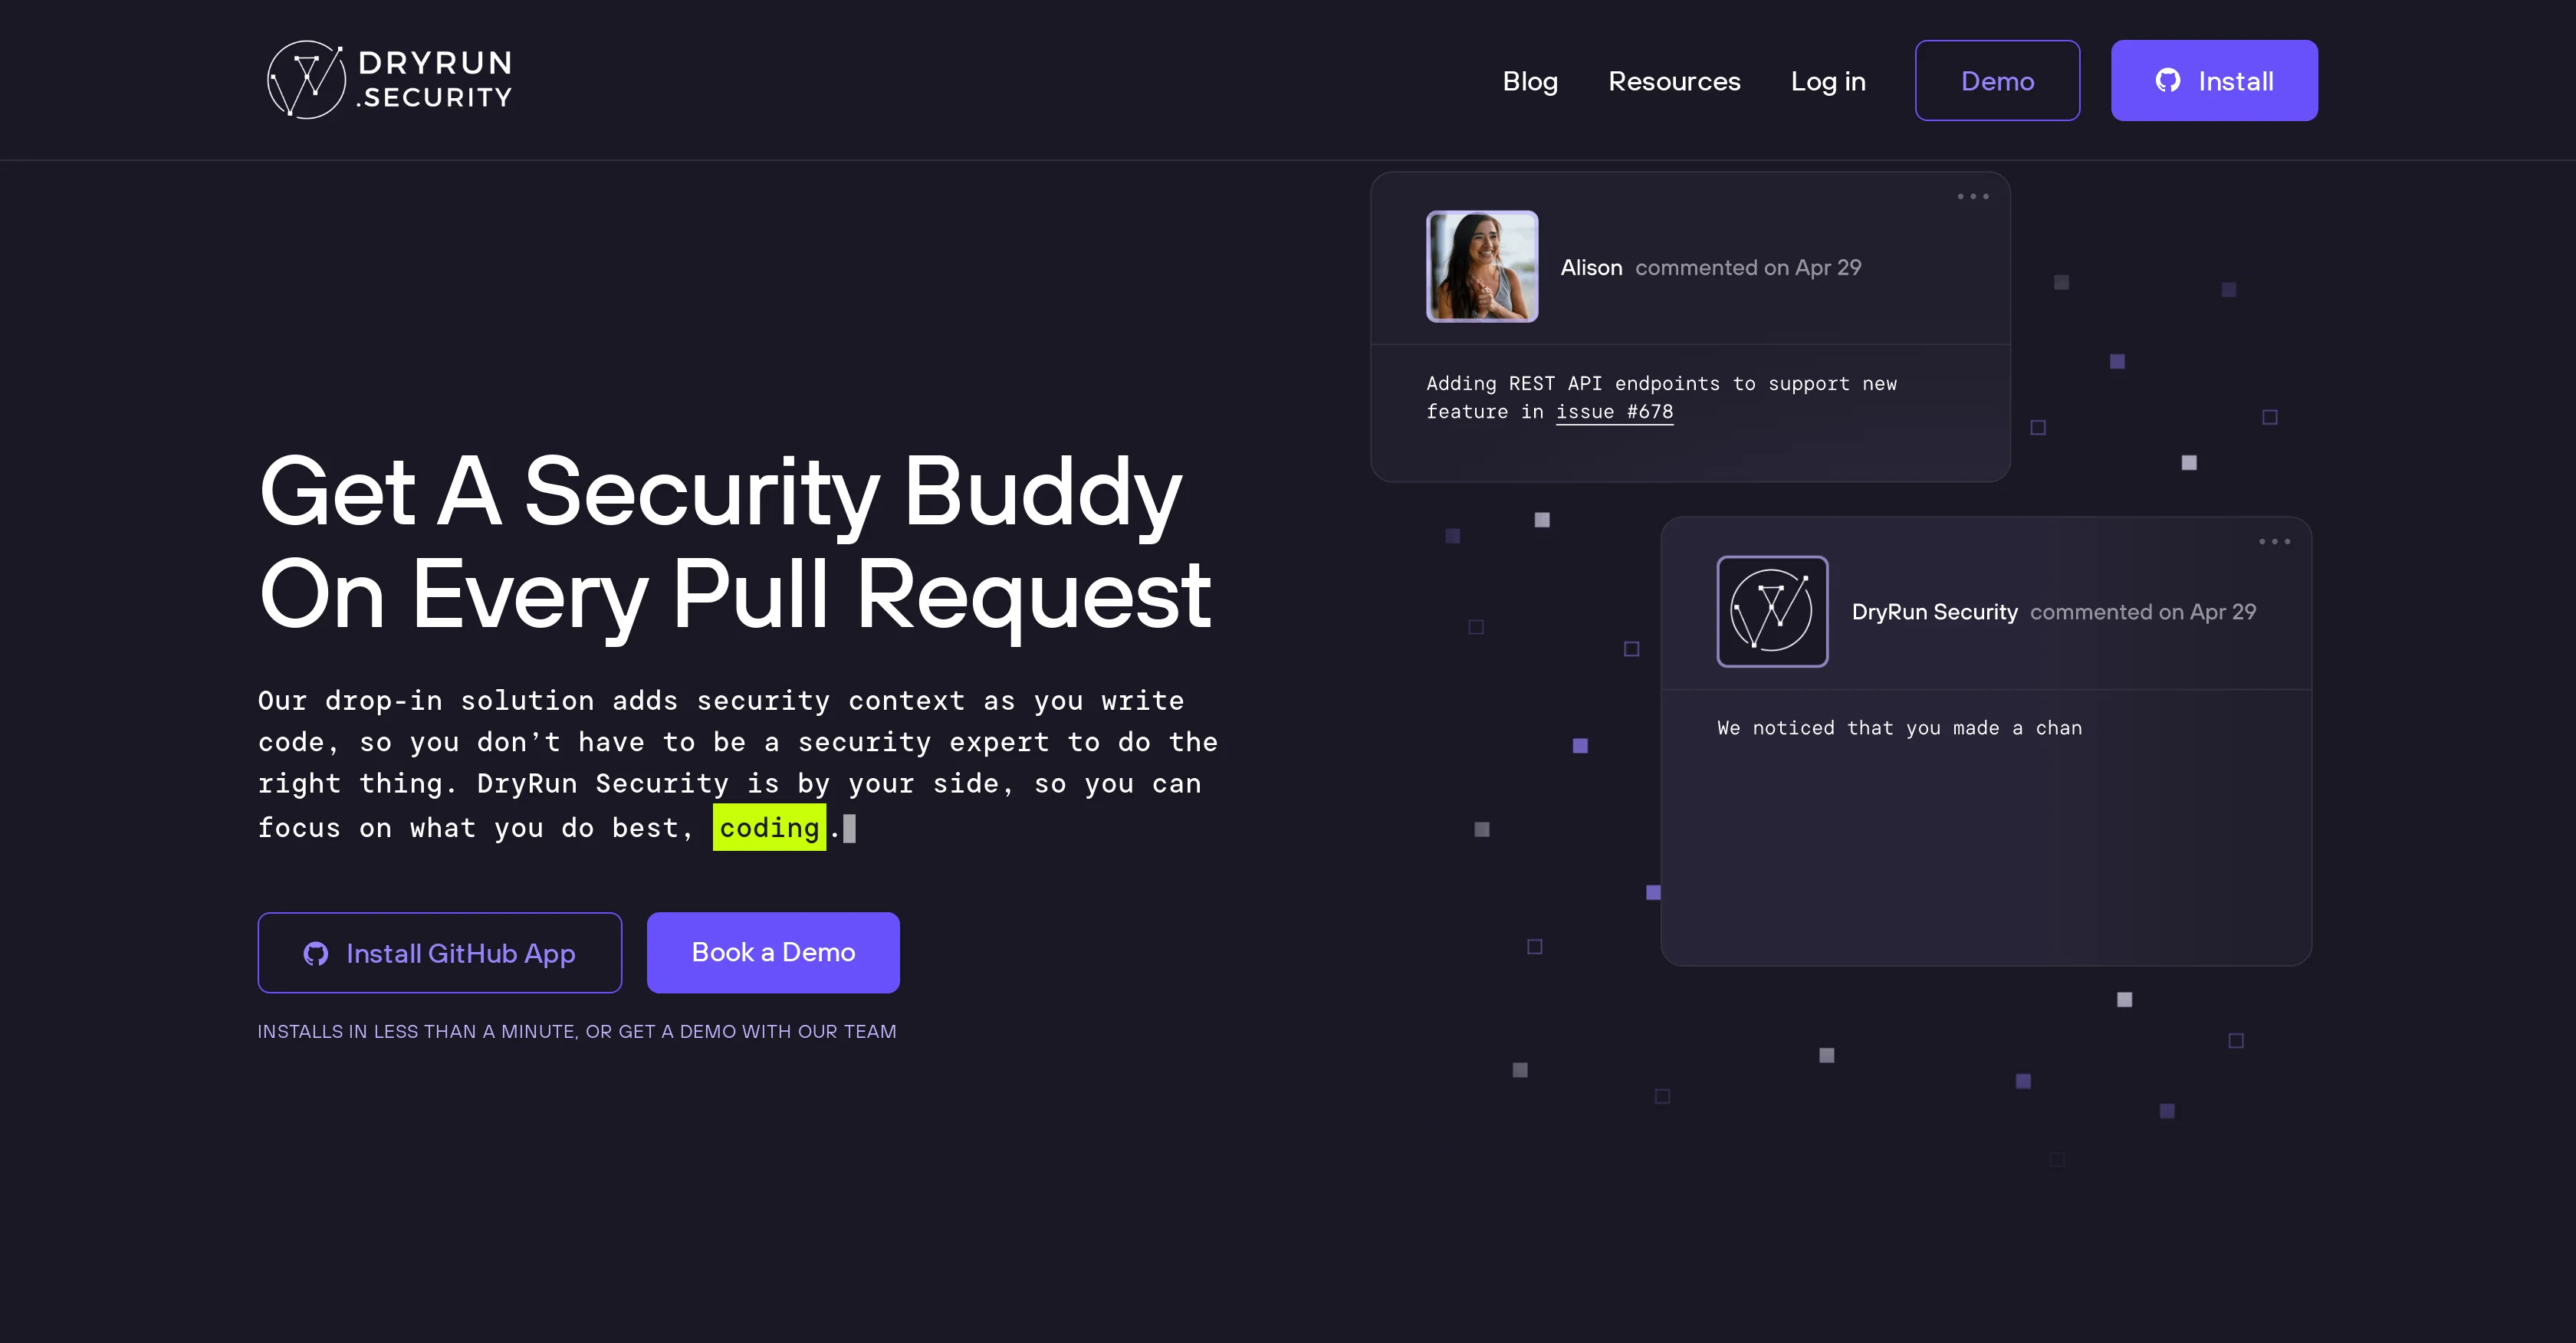
DryRun Security is an AI-powered tool designed to support developers by providing automated in-line security checks during the coding process. Aimed at implementing a 'security buddy' in your coding workflow, it reinspects every code change as a pull request taking place, enabling developers to work faster and more safely.
Its core focus is in providing a 'security context' to the developers, assisting them in understanding the impact of the code changes they're making, right as a pull request is opened.
DryRun Security uses a mechanism called 'Contextual Security Analysis' to examine each pull request, which assists in reducing the frustrations often caused by repetitive alerts or inaccurate results in many other security testing applications.
The tool is designed to support a variety of languages and frameworks including Rails, Express, Golang, Python, Node.js, Next.js and Javascript, with more to be added.
The security features examined include Authentication and Authorization, Sensitive Codepaths, Sensitive Functions, Authorship and Intent, and Code Brittleness.
The tool provides quick installation as a GitHub App and fast security reviews for code changes to enable faster merging. Furthermore, it offers a protection layer for every source code repository in your organization, helps to increase the velocity of the development pipeline, and thus enhances developer productivity.
Access & connections
Where you can use DryRun Security, and what it plugs into.
Platforms
Integrations
Capabilities
What this tool accepts, produces, and is strongest at.
Input
- API
- Code
Output
- Code
- API
Supported features
- Code Review
Pros & cons
Pros
- Automated in-line security checks
- Supports multiple languages and frameworks
- GitHub App quick installation
- Fast security reviews
- Protects every code repository
- Increases development pipeline velocity
- Contextual Security Analysis
- Reduced false positives
Show 11 more
- Examines Authentication and Authorization
- Examines Sensitive Codepaths
- Examines Sensitive Functions
- Examines Authorship and Intent
- Examines Code Brittleness
- Near real-time feedback
- Developer-friendly interface
- Checks every code change
- Security context delivered pre-merge
- Automated security context
- Works with code repositories
Cons
- Limited to GitHub repositories
- Missing support for some languages
- Limited accuracy details provided
- Reliance on pull request workflow
- Unknown performance on large projects
- Potentially overgeneralized security analysis
- Limited customization options
- Lack of enterprise features
Show 2 more
- In beta, potential instability
- Lack of detailed technical documentation
Compare alternatives
Similar tools in the catalog — with a clear reason to open each one.

ZeroPath ✓
FreemiumAI-native SAST finding 2x more vulnerabilities with fewer false positives.
Why look Higher community rating
Full comparison

Endor Labs ✓
UnknownAI-powered application security that prioritizes real risks.
No pricing
Full comparison
Releases 1
FAQ 12
What is DryRun Security?
How does DryRun Security work?
What are some key features of DryRun Security?
How does DryRun Security aid in the coding process?
What does 'security context' mean in terms of DryRun Security?
What is 'Contextual Security Analysis' in DryRun Security?
What programming languages and frameworks does DryRun Security support?
What security features does DryRun Security examine?
How does DryRun Security integrate with GitHub?
How fast is DryRun Security's review process?
What benefits does DryRun Security provide for my development pipeline?
Does DryRun Security offer protection for every source code repository?
Related tools
Recommended
Marblism ✓
FreemiumAI Employees who Work for Your Business

CodeAnt AI ✓
Free TrialAI to detect & auto-fix bad code

Agentgpt ✓
FreemiumDeploy autonomous AI Agents effortlessly in your browser.
Hyperis ✓
FreemiumOrganized task prioritization.
AutoGPT ✓
Free TrialRun AutoGPT in your browser for free
Archie ✓
FreemiumThe platform to architect, build, and run production-grade applications.