
Security audits vv2.0.0 2026 Rank: #246
AI QA Monkey ✓
Instant AI Security Score: Scan Free, Fix with AI, Monitor 24/7.
Verdict
A quick read before you dig into the full page.
- Best if
- Instant AI Security Score: Scan Free, Fix with AI, Monitor 24/7
- Skip if
- Free scan shows a findings preview only; complete evidence, fixes and exports are unlocked with a paid report
- Pick this when
- Runs 100+ proprietary security checks across 15 attack surfaces in under 60 seconds — free, no signup, no credit card
Considering SecureSaaS instead? Compare side by side
Overview
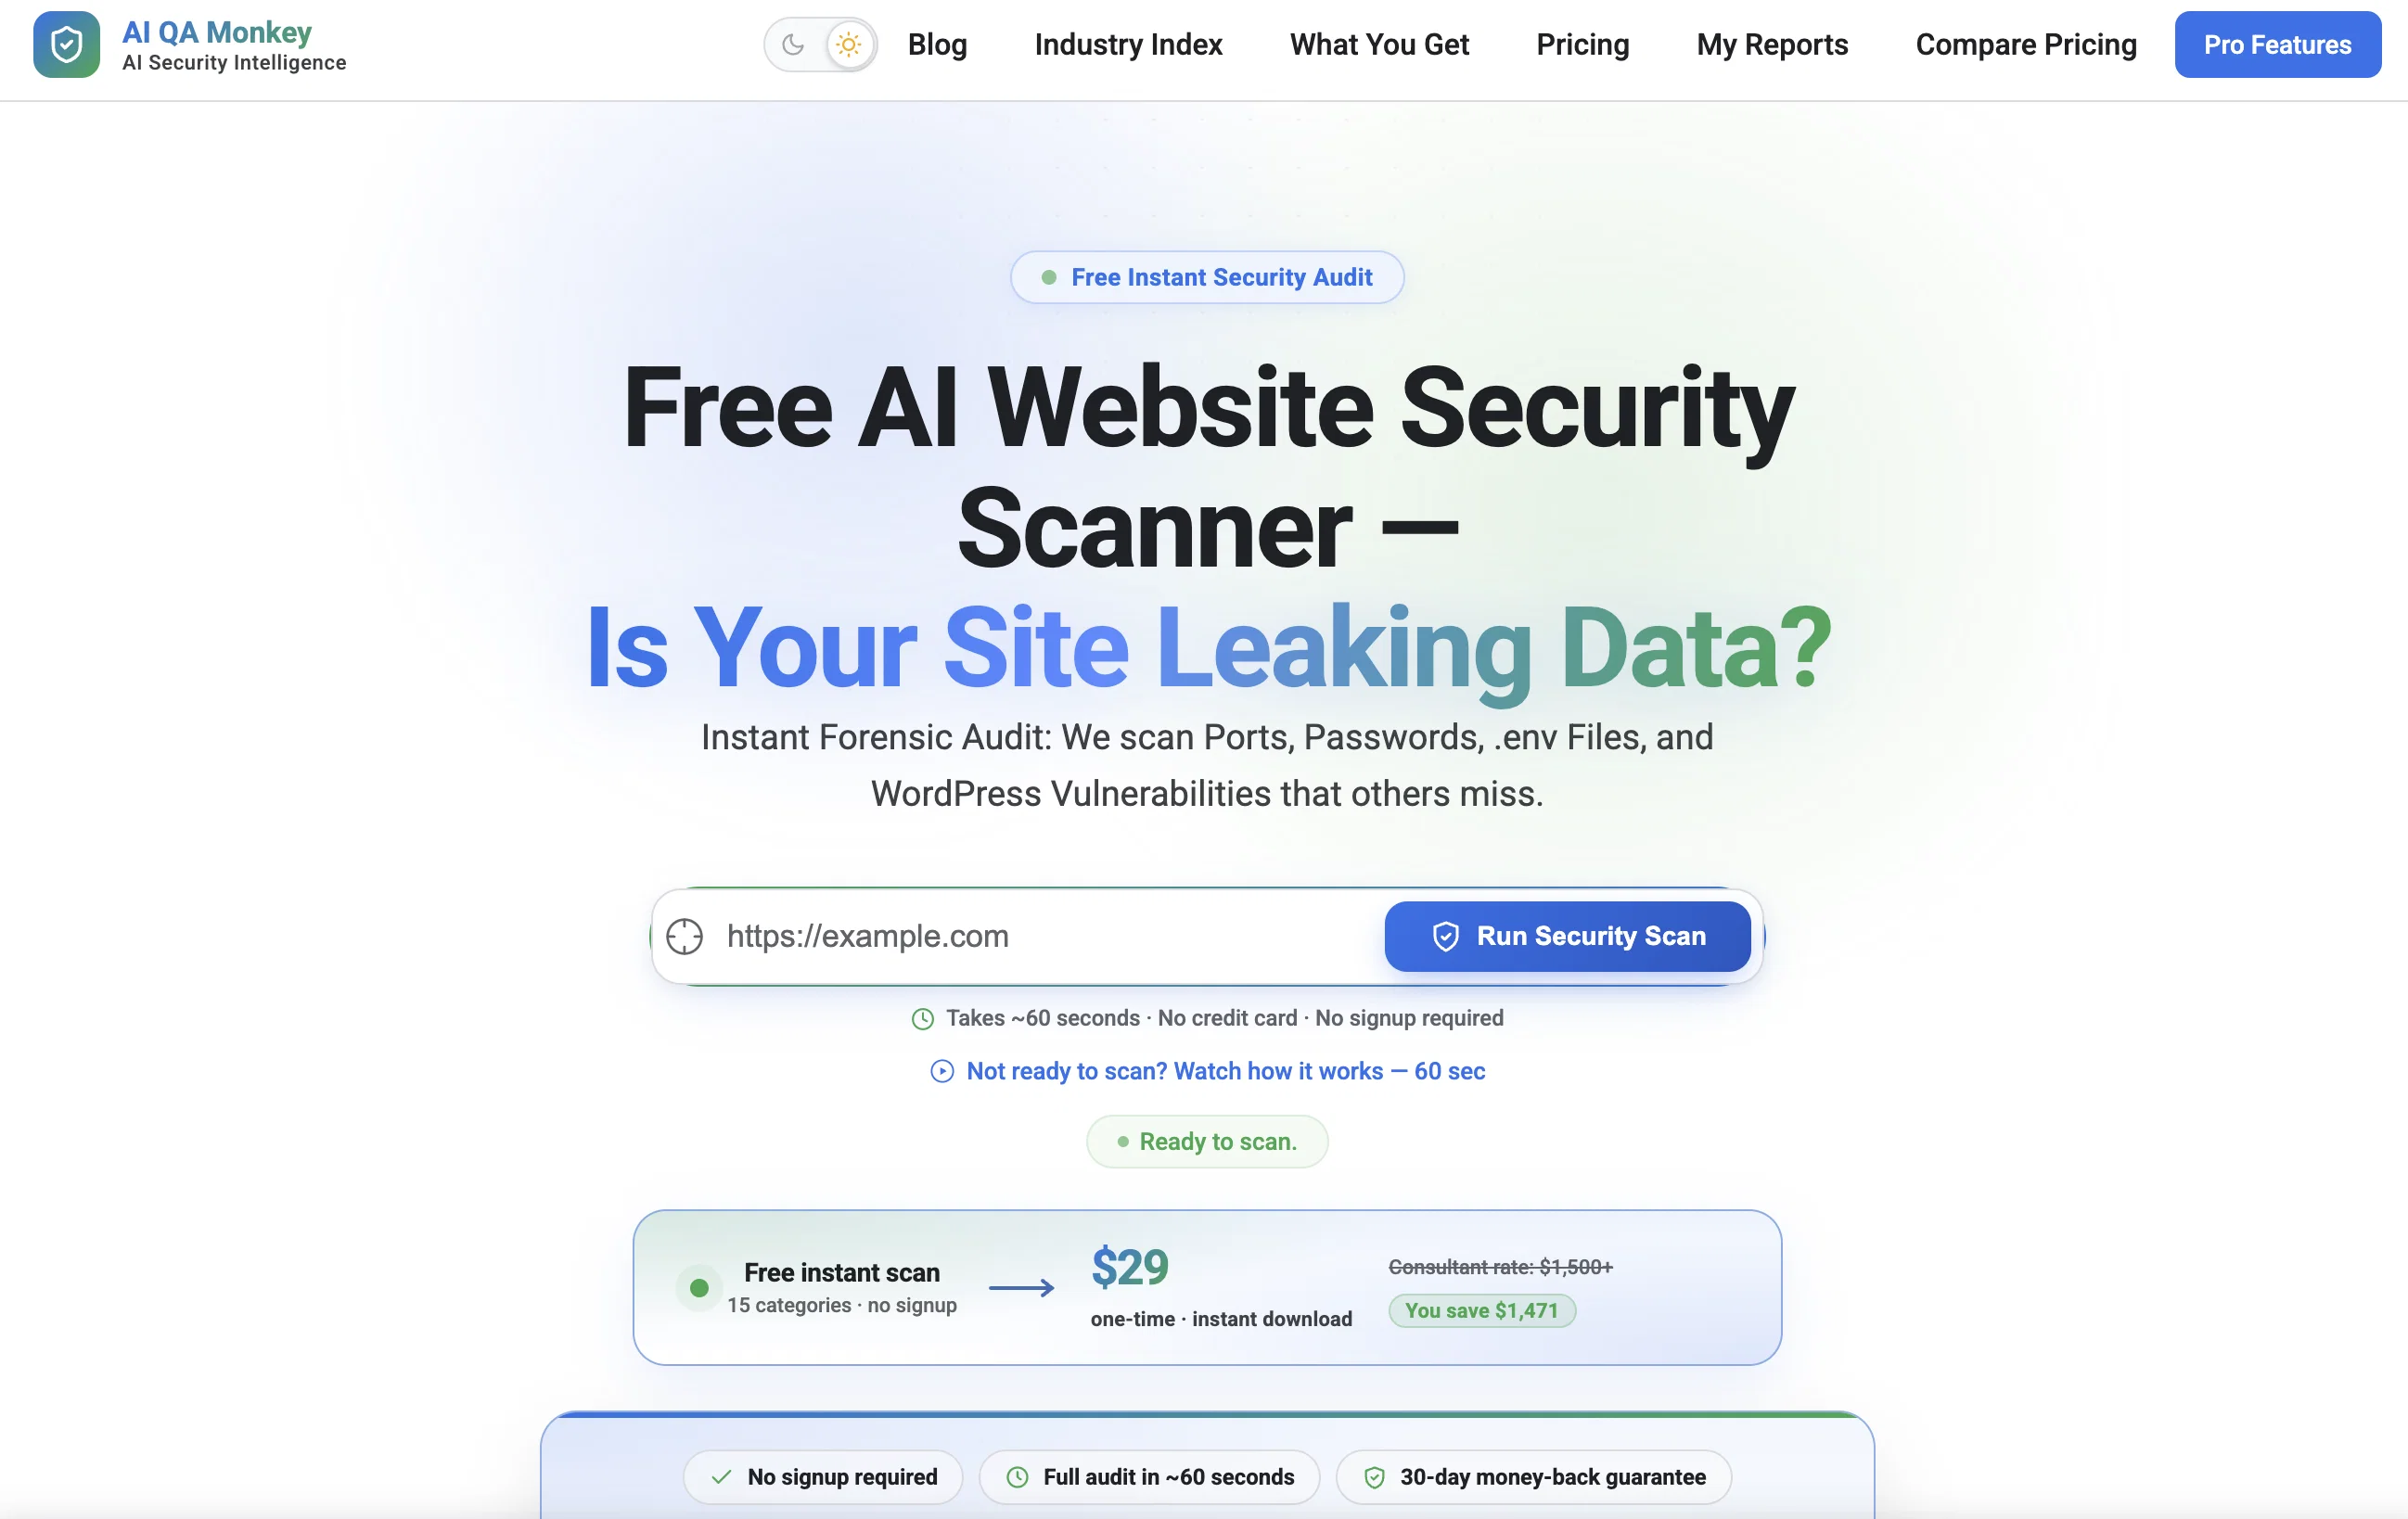
Paste any URL and receive a complete forensic security audit in about 60 seconds — free, no signup, no credit card. A professional penetration test costs $1,500–$5,000 and takes weeks. We compress that into one minute and 100+ automated checks across your entire external attack surface.
━━ WHAT WE INSPECT ━━
TRANSPORT & ENCRYPTION. Full SSL/TLS validation — certificate chain, issuer, expiry countdown, signature algorithm, negotiated protocol version, and weak-protocol / expiring-cert alerts. HSTS strength analysis (max-age, includeSubDomains), HTTPS-redirect enforcement, and mixed-content detection.
SECURITY HEADERS. A graded A–F audit of ten headers — Content-Security-Policy, Strict-Transport-Security, X-Content-Type-Options, X-Frame-Options, Referrer-Policy, Permissions-Policy, and the full Cross-Origin trio (COOP, COEP, CORP). We parse your CSP for real weaknesses — unsafe-inline, unsafe-eval, wildcard sources, report-only-not-enforced — and flag clickjacking exposure and server-version leakage.
REAL-TIME PORT SCANNING — ON OUR OWN INFRASTRUCTURE. This is the engine we built ourselves. We don't resell a stale, weekly-refreshed threat database like most scanners. We operate dedicated nmap-backed scanning infrastructure that probes 19 high-risk ports live on every free scan — SSH, RDP, MySQL, PostgreSQL, MongoDB, Redis, Elasticsearch, SMB, cPanel, mail services and more — and recognizes 40+ services. Premium unlocks a full sweep of all 65,535 ports. When an exposed service maps to a known CVE, we surface it. Shared-hosting and CDN-edge aware, so you see your true origin exposure, not false positives.
EXPOSED FILES & LEAKED SECRETS. Parallel probing of sensitive paths — .env and its variants, .git/HEAD and config, .svn, wp-config backups, SQL dumps, .htpasswd, phpinfo, adminer, debug logs, server-status. Plus live client-side secret detection: private keys, AWS access keys, Stripe live keys, SendGrid, GitHub and Slack tokens, and Google API keys sitting in your HTML and JS bundles. Plus exposed JavaScript source maps that hand attackers your original source.
SUPPLY-CHAIN & MAGECART DEFENSE. The #1 way modern sites get breached. We flag compromised or abandoned third-party CDNs (polyfill.io-class attacks), missing Subresource Integrity on cross-origin scripts, and card-skimmer injection risk — and we fingerprint your front-end libraries (jQuery, Bootstrap, Lodash, Handlebars, Axios, Moment.js) against a curated CVE table, naming the exact patched version.
DNS, EMAIL TRUST & REPUTATION. A complete email-spoofing defense audit — SPF with policy strictness, DKIM across nine common selectors, DMARC enforcement level, plus MTA-STS, TLS-RPT, BIMI and CAA. Real-time domain reputation and blacklist checks, and DNS record analysis.
ATTACK SURFACE & RECON. Subdomain enumeration via certificate-transparency logs with dangling-CNAME takeover detection across 14 cloud providers. CORS misconfiguration and origin-reflection (including the critical wildcard-with-credentials case), dangerous HTTP methods (PUT, DELETE, TRACE), GraphQL introspection, and Swagger/OpenAPI endpoint discovery. Technology fingerprinting (CMS, server, framework versions), WAF detection (Cloudflare, AWS WAF, Sucuri, Akamai, Incapsula), CDN identification, and cloud-storage reference detection (S3, Azure Blob, GCS).
WORDPRESS & CMS. User enumeration, xmlrpc.php exposure, plugin detection, version disclosure via readme, and wp-config backup exposure — the WordPress attacks basic scanners skip.
COOKIES & SESSIONS. Secure, HttpOnly and SameSite flag analysis on session cookies.
━━ BUILT FOR YOUR STACK ━━
Beyond the universal scan, dedicated deep scanners tune every check to your framework — WordPress, Shopify, React, Next.js, Angular, Laravel, Drupal and Joomla, plus focused API/CORS, open-port, DNS/SPF/DMARC and compliance scanners. Next.js apps get SSRF and NEXT_PUBLIC_ leak checks; Laravel gets APP_DEBUG and exposed Telescope/Horizon detection; Drupal gets Drupalgeddon coverage — the vulnerabilities that only matter on your platform.
━━ HOW IT SCORES ━━
Every finding is ranked Critical / High / Medium / Low / Info and rolled into a weighted 0–100 security score across six categories — Application, Infrastructure, Transport, Email, Compliance and Reputation — with an estimated score-after-fix so you know the payoff before you touch a line. A dedicated compliance engine maps your posture to OWASP Top 10 (2021), PCI DSS v4.0, ISO 27001 Annex A, SOC 2 Type II and GDPR technical controls, with a per-framework readiness score.
━━ HOW YOU FIX IT ━━
Finding problems is easy. We're obsessed with closing them. Every single vulnerability ships with four things: a tested copy-paste server config (Apache / Nginx / WordPress), an AI Fix Prompt engineered for ChatGPT, Claude and Cursor, a difficulty rating and estimated fix time ("Easy, ~20 min"), and a step-by-step plain-English playbook — backed by a library of 45+ in-depth remediation guides. You don't need a security team. You need 20 minutes and a clipboard.
━━ HOW YOU STAY SECURE ━━
Hackers don't scan you once, so neither do we. 24/7 continuous monitoring re-scans your site automatically and emails you the moment your score drops or a new vulnerability appears — before attackers find it. Every one-time report includes 30 days of monitoring, free.
━━ HOW YOU PROVE IT ━━
Score 80+ and claim your free Verified Security Badge — a live, database-verified trust seal that embeds with one line of HTML, updates on every scan, and lets visitors click through to watch your site pass a live audit. Turn security into a sales asset.
━━ THE REPORT ━━
A twelve-section dashboard and boardroom-ready PDF: security score gauge, severity distribution, full vulnerability table with evidence, kill-chain analysis, interactive Attack Surface Map (rendered as a live network graph in both the dashboard and the PDF), compliance mapping, copy-paste fixes, AI fix prompts, executive summary, trend view, evidence mode, and one-click export to white-label PDF, JSON and CSV. Everything lives in the My Reports portal — passwordless access from any device with a one-time email code.
━━ PRICING ━━
Free scan, forever. Full report — $29 one-time per domain, yours to keep. Pro — $29/mo with up to 30 reports per domain and the Verified badge. Agency — $79/mo for a 10-domain portfolio. Risk-free: full refund if your security rating doesn't improve within 30 days.
Your site is either verified secure — or it's an open question. Find out in 60 seconds.
- Free Instant Scan
- Vulnerability Detection
- White-label Pdf Reports
- Gdpr & Compliance Check
- Fix Recommendations
Best for
Short scenarios where AI QA Monkey tends to shine.
-
Instant AI Security Score: Scan Free, Fix with AI, Monitor 24/7.
Example outputs 1
Sample generations and before/after results for AI QA Monkey.
Access & connections
Where you can use AI QA Monkey, and what it plugs into.
Platforms
Integrations
Capabilities
What this tool accepts, produces, and is strongest at.
Input
- Text
Output
- Text
Highlights
- Agents
- API
- No Signup
Supported features
- Agents
- API
- No Signup
- QA Automation
Pros & cons
Pros
- Runs 100+ proprietary security checks across 15 attack surfaces in under 60 seconds — free, no signup, no credit card
- Real-time open-port scanning on our own dedicated infrastructure — probed live on every scan, never stale cached data
- 24/7 continuous monitoring with instant email alerts the moment your score drops or a new vulnerability appears
- Every finding ships with a copy-paste server fix and an AI Fix Prompt ready for ChatGPT, Claude & Cursor
- Difficulty rating and estimated fix time on every finding, so you can triage at a glance
- Framework-tuned deep scanners for 8 stacks — WordPress, Shopify, React, Next.js, Angular, Laravel, Drupal & Joomla
- Interactive Attack Surface Map rendering your full external footprint: subdomains, open ports, exposed files and WAF status
- Kill-chain analysis — reconstructs the exact reconnaissance path an attacker would walk through your exposure
Show 40 more
- Deep sensitive-file leak detection — .env and .git, wp-config backups, SQL dumps, .htpasswd and debug logs
- Client-side secret detection — AWS, Stripe, GitHub, Slack, SendGrid and Google keys exposed in your HTML and JS bundles
- Source map and build-artifact exposure detection — before attackers get your original source
- Supply-chain & Magecart defense — flags compromised third-party CDNs, missing Subresource Integrity and skimmer injection hosts
- Known-CVE scanning of front-end libraries with the exact patched version named
- API & CORS attack-surface hardening — credentialed wildcard CORS, origin reflection, dangerous HTTP methods, GraphQL introspection and Swagger/OpenAPI exposure
- Dedicated API key leak detection across 30+ SaaS providers
- WordPress & CMS deep scan — plugin detection, user enumeration and xmlrpc.php vulnerability checks
- Subdomain enumeration via certificate-transparency logs
- Dangling-DNS subdomain takeover detection across 14 cloud providers
- Full 65,535-port sweep on premium — complete port inventory with service, version and CVE mapping
- Exposed-database detection — MongoDB, Redis, Elasticsearch, Memcached and CouchDB left open to the internet
- Real-time CVE mapping on every exposed service
- Shared-hosting and CDN-edge aware scanning — separates your true origin exposure from provider infrastructure to eliminate false positives
- WAF & CDN detection — Cloudflare, AWS WAF, Sucuri, Akamai and Incapsula, with what's protected versus exposed at the origin
- Technology fingerprinting — CMS, server, framework versions and CDN
- Full SSL/TLS validation — certificate chain, issuer, expiry countdown, signature algorithm and weak-protocol alerts
- HSTS strength analysis, HTTPS-redirect enforcement and mixed-content detection
- A–F security-headers grade across 10 headers, including the full Cross-Origin trio (COOP, COEP, CORP)
- CSP deep-parse — flags unsafe-inline, unsafe-eval, wildcard sources, report-only-not-enforced and clickjacking exposure
- Cookie & session security audit — flags session cookies missing Secure, HttpOnly or SameSite
- HTTP/2 and protocol analysis
- Full email trust suite — SPF, DKIM, DMARC, BIMI, MTA-STS & TLS-RPT in a single pass
- DKIM validation across 9 common selectors and DMARC enforcement-level analysis
- Real-time domain reputation and blacklist monitoring
- DNS and CAA record security analysis
- Cloud storage exposure detection — referenced AWS S3, Azure Blob and Google Cloud Storage buckets
- Category-based risk scoring with severity badges, trend history and confidence levels
- Estimated score-after-fix on every finding — see how many points each remediation earns before you touch a line of code
- Compliance mapping to OWASP Top 10, PCI DSS v4.0, ISO 27001, SOC 2 and GDPR with a per-framework readiness score
- Evidence Mode — full HTTP response captured as proof (status code, server header, TLS version), so every result is verifiable
- 45+ in-depth remediation playbooks plus free unlimited re-scans for 30 days to confirm each fix landed
- Free embeddable Verified Security Badge — live, database-verified score with tiers at 80+, 90+ and 95+
- My Reports portal — passwordless one-time email code gives access to all your reports from any device
- Multi-domain portfolio management on Agency plans
- Boardroom-ready branded PDF reports with plain-English executive summaries for stakeholders
- Developer-workflow exports — JSON and per-finding CSV into Jira, Linear and CI/CD, or paste straight into Cursor and ChatGPT
- Share results in one click to X, LinkedIn or a direct link
- Non-intrusive external assessment — no agent, no install, no code access required, 100% cloud-based
- Cost-effective — a $29 one-time report replaces a $1,500+ consultant audit
Cons
- Full remediation report requires payment — $29 one-time per domain, or a Pro subscription ($29/mo) that covers up to 30 full reports per month per domain
- Free scan shows a findings preview only; complete evidence, fixes and exports are unlocked with a paid report
- Expert-level full report generation costs $29 per domain
- Multi-domain portfolio management requires the Agency plan (up to 10 domains)
- Verified Security Badge is available only to sites scoring 80 or higher
Compare alternatives
Similar tools in the catalog.
People also view
Tools that often show up alongside AI QA Monkey in collections and comparisons.
SecureSaaS ✓
FreemiumFree website vulnerability scanner for web apps.
SchemaGen ✓
FreemiumDeploy schema without the dev tickets.
AISafe Labs ✓
FreemiumAI agents that assess your app with hacker expertise at machine speed.
Jason AI ✓
PaidAI-powered assistant for B2B sales outreach

Grok ✓
FreemiumConversational AI for understanding the universe.
freebeat AI ✓
FreemiumTurn Music & Ideas into Viral Videos In One Click
DeepSeek ✓
FreeUnravel the mystery of AGI with curiosity
Claude ✓
FreemiumBuilding reliable, interpretable AI systems
Releases 3
🚀 AI QA Monkey v2.0.0 is Live: From One-Time Audit to Unstoppable 24/7 Defense.
This is our most massive upgrade yet. We haven't just updated our engine—we've quadrupled our security coverage. Scaling from our original 25 checks, we now deploy 100+ proprietary security tests that most competitors miss.
But the biggest breakthrough? True 24/7 Continuous Monitoring. Your website is now constantly guarded. Hackers don't sleep, and neither do we. As new malware, vulnerabilities, and zero-day threats emerge globally, our engine is instantly updated. If your site is exposed to a newly added threat, you receive an immediate alert—allowing you to patch the hole before attackers even know it's there. Every finding now ships with copy-paste fixes, AI remediation prompts, and a step-by-step guide.
🔹 Release Notes (What's New — v2.0.0)
🛡️ AI QA Monkey v2.0.0 — "Always-On Security" Transforming a static audit into a living, breathing, and guided security shield.
🔍 Detection — 4X Coverage Expansion (100+ Tests) Coverage has quadrupled. We now run over 100 deep-scan checks across 15 attack surfaces, including 70+ proprietary tests unavailable in competing tools.
We aggressively target the newest malware and emerging vulnerabilities:
-
Supply-Chain & Magecart Defense: Detects compromised or abandoned third-party CDNs silently executing malicious code in your visitors' browsers.
-
Zero-Day & Known CVE Library Scanning: Instantly flags vulnerable front-end libraries the moment they become a threat.
-
Client-Side Secret Detection: Hunts down leaked API keys and tokens hidden deep in your JS bundles.
-
Source-Map & Build Exposure: Prevents disastrous leaks by catching production source maps that hand attackers your raw code.
-
Complete Email-Trust Suite: Validates SPF, DKIM, DMARC, BIMI, MTA-STS & TLS-RPT in a single, powerful pass.
-
Advanced Web Architecture Checks: Reflected-origin CORS, dangerous HTTP methods, GraphQL introspection, CAA & HSTS-strength validation.
🔔 The Game Changer: 24/7 Continuous Monitoring (NEW) Set it and forget it. We continuously monitor your site around the clock. Our threat engine is constantly updated with new checks for the latest malware and exploits. If your security score drops or our engine detects a newly discovered vulnerability on your site, you get an immediate email alert—stopping regressions in their tracks.
🗺️ Visibility — See What The Attackers See Our interactive Attack Surface Map visually renders your entire external footprint—subdomains, open ports, exposed files, and WAF status—as a live network graph, beautifully integrated into your web dashboard and PDF reports.
🧠 AI-Driven Remediation Intelligence Finding the problem is only half the battle. Every vulnerability now comes with copy-paste server configs, an AI Fix Prompt (ready for ChatGPT, Claude, or Cursor), and a plain-English step-by-step guide backed by a library of 45+ deep-dive remediation playbooks.
📄 Industry-Leading, Boardroom-Ready Reports Generate stunning audits in seconds: severity-ranked findings, compliance mapping (OWASP · PCI DSS · ISO 27001 · GDPR), score trends, and confidence levels, fully exportable to PDF, JSON, or CSV.
💼 Plans Scaled for Every Workflow (NEW)
- One-Time Report — $29 (Yours to keep)
- Monitor — $7.99/mo (Always-on early warning system)
- Pro — $29/mo (Monitoring + 30 full reports/domain)
- Agency — $79/mo (Up to 10 domains + 300 full reports/domain)
♻️ An Engine That Never Stops Learning As fresh CVEs, malware, and attack techniques emerge, we code the detections straight into our engine—automatically. Your scans always test against the absolute latest threats. No installations, no maintenance. Just pure security.
🔹 One-liner (Tagline)
AI QA Monkey v2.0.0: Scan. Fix. Monitor. On Repeat. 100+ deep checks, a live attack-surface map, and relentless 24/7 monitoring that catches new threats before they strike.
Since launch, our platform’s website testing coverage has tripled, with the addition of advanced capabilities such as Attack Surface Map, over 70 proprietary tests not offered by competing solutions, and a comprehensive, industry-leading security report built to the highest standards of technical depth and coverage. The latest release significantly expands detection, visibility, and remediation intelligence across the entire attack surface.
Imported reviews 3
This is the best ai
Best AI tool
Great tool for quickly assessing any security risks that may be present on a site. Also made a video about it https://www.youtube.com/watch?v=yfHd-vWsUkc
FAQ 12
What does AI QA Monkey do?
What types of vulnerabilities does AI QA Monkey scan for?
How does AI QA Monkey help secure headers and SSL?
How does AI QA Monkey detect object leaks?
What is the role of AI QA Monkey in GDPR compliance checks?
Can AI QA Monkey perform open port discoveries such as SSH, FTP, MySQL?
Does AI QA Monkey offer real-time domain reputation analysis?
What is the feature of Multi-Domain Dashboard in AI QA Monkey?
How does AI QA Monkey calculate an overall risk score?
Can AI QA Monkey generate professional reports?
How does AI QA Monkey perform CMS vulnerabilities detection?
Can AI QA Monkey scan multiple domains simultaneously?
Related tools
Recommended

Averi AI ✓
Free TrialThe AI Content Engine for Startups
ChatGPT ✓
FreemiumAsk anything, create anything, and move from idea to action.
Automateed ✓
Free TrialCreate eBooks effortlessly with Automateed, the AI-powered writing tool.

Notis ✓
Free TrialThe first WhatsApp assistant that runs on your ChatGPT and Claude subscriptions
Claude ✓
FreemiumBuilding reliable, interpretable AI systems
Jason AI ✓
PaidAI-powered assistant for B2B sales outreach