
Pentesting 2026 Rank: #995
AISafe Labs ✓
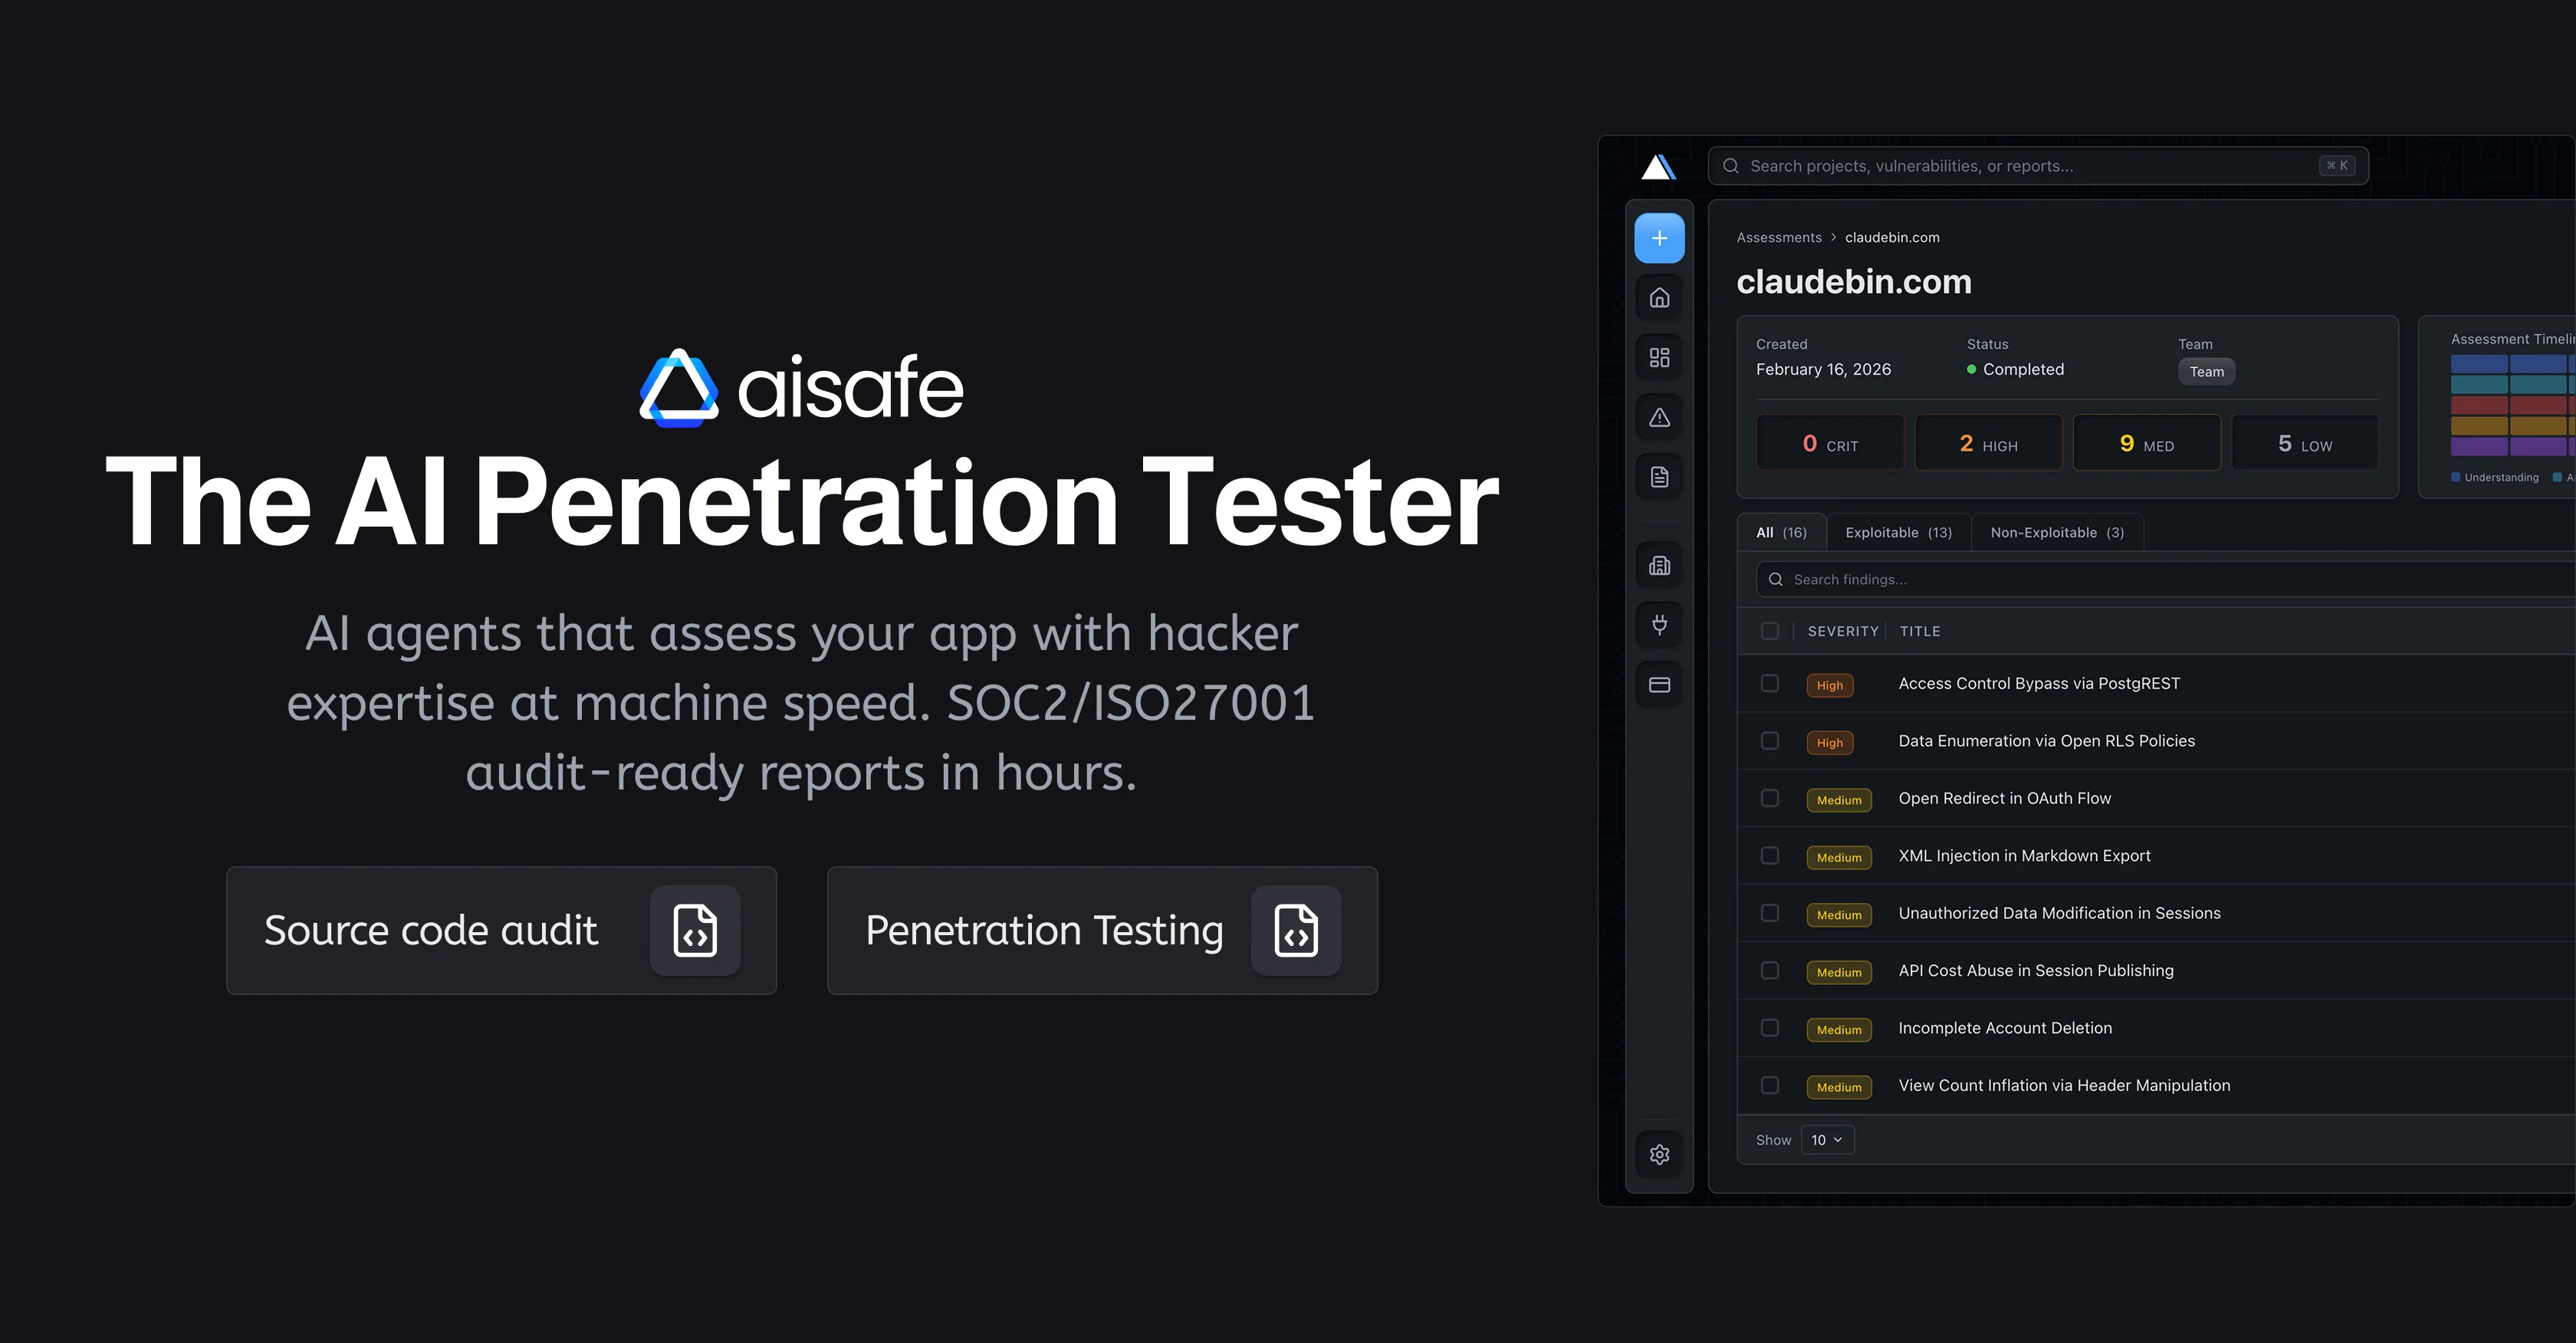
AI agents that assess your app with hacker expertise at machine speed.
Verdict
A quick read before you dig into the full page.
- Best if
- AI agents that assess your app with hacker expertise at machine speed
- Skip if
- Limited integration options
- Pick this when
- On-demand security assessments
Considering HackerAI instead? Compare side by side
Overview


AISafe Labs provides on-demand security assessments for web applications. The platform employs AI-based pen testers and source code auditors, offering comprehensive safety solutions across various environments.
Their services include performing source code audits, where they discover vulnerabilities in applications, such as business logic flaws, authorization weaknesses, and insecure data flows.
They combine source code analysis with live environment testing under what they term 'White-Box Pentest' to expose weaknesses and propose fixes. AISafe Labs also offer 'Black-Box Pentest', a service that assesses your application from an attacker's perspective, thereby discovering and chaining vulnerabilities in a live environment.
AISafe Labs makes use of a unique methodology in conducting security assessments, applying advanced security expertise rather than using predefined checklists.
The security services integrate smoothly with users' existing CI/CD pipelines, GitHub, GitLab, Jira, and Linear without disrupting workflows. Furthermore, the platform offers dependency tracking, source-to-sink analysis, user permission models, and architectural overview across the full stack.
AISafe Labs provides detailed, audit-ready reports (SOC2/ISO27001) that reflect resolved security issues and remaining risks.
Access & connections
Where you can use AISafe Labs, and what it plugs into.
Platforms
Capabilities
What this tool accepts, produces, and is strongest at.
Input
- API
- Code
- Text
Output
- Code
- API
- Text
- Image
Highlights
- SOTA
- Agents
- API
Supported features
- Agents
- API
Models
Text
Image
Video
Coding
Pros & cons
Pros
- On-demand security assessments
- White-Box Pentest service
- Black-Box Pentest service
- Source code audits
- Vulnerability discovery
- CI/CD pipeline integration
- Github integration
- Gitlab integration
Show 43 more
- Jira integration
- Linear integration
- Dependency tracking feature
- Source-to-sink analysis
- User permission models
- Architectural overview feature
- Audit-ready reports
- SOC2 Compliance
- ISO27001 Compliance
- Confidential secrets protection
- NIS2 Compliance
- Trusted boundaries validation
- Continuous security monitoring
- Advanced against the threat assessment
- Attack paths identification
- Detailed security reports
- Audit-ready reports in hours
- Identifies business logic flaws
- Identify authorization weaknesses
- Detects insecure data flows
- Real exploits validation
- Provides security solutions for every environments
- Identifies architectural vulnerabilities
- Permission bypasses discovery
- Authentication flaws discovery
- Privilege escalation paths discovery
- Threat model creation
- Patch Validation
- False positives close to zero
- Reproducible findings
- Endpoint monitoring feature
- Security invariants validation
- Efficient cost analysis
- Secured clients tracking
- Tailored security services
- Suitable for stakeholder communication
- Continuous Pull Request Review
- Testimonials availability
- Reports suitable for compliance work
- Sensitive data encrypted
- Free plan availability
- Clear security insights translation
- Parallel agents for attacks
Cons
- No predefined checklists
- No mention of compatibility
- Lack of multi-language support
- Limited integration options
- Assessment scope user-defined
Compare alternatives
Similar tools in the catalog.


Releases 1
Imported reviews 3
I’ve used AISafe extensively and have already discovered more than five CVEs with its help. It’s an absolute beast when it comes to identifying potential vulnerabilities directly in source code.
Of course, you still need to manually test and validate the findings, as you would with any security tool, but it does a great job of pointing you toward issues that are genuinely worth investigating. Overall, it has saved me a lot of time and has become a valuable part of my vulnerability research workflow.
Used both personally and adapted it for use in a professional setting. I really enjoy using it.
So far, it has led us to discover and publish over 10 CVEs. In a professional setting, the source code review helped us reduce time per project and allowed our team to take on more work and do it more efficiently. A must-have for both the security researcher and the workspace.
I have used AISAFE a lot for security research involving WordPress plugins and CVE-related submissions through the Wordfence program.
Pros:
+ Great with mapping important parts of codebase and highlighting the areas worth looking into.
+ Reduces a lot of time spent searching trough bloat unrelated code.
+ Makes the whole manual testing part a lot easier.
+ Useful for pentesters, bug bounty hunters or any type of source-code audits.
Cons:
- Some leads might not be exploitable and manual trimming is still required.
Overall AISAFE is a great skill MULTIPLIER for any pentester, it wont replace you but it will make you better at it.
FAQ 12
What is AISafe Labs?
What does AISafe Labs do?
Who typically uses AISafe Labs?
What is the 'White-Box Pentest' offered by AISafe Labs?
How does 'Black-Box Pentest' work in AISafe Labs?
Can AISafe Labs identify business logic flaws and authorization weaknesses?
What is AISafe Labs methodology for conducting security assessments?
Does AISafe Labs integrate with CI/CD pipelines and other tools like Github, Gitlab, and Jira?
Can AISafe Labs perform Dependency Tracking and Source-to-Sink analysis?
What types of reports does AISafe Labs provide?
Does AISafe Labs ensure SOC2 and ISO27001 compliance?
How does AISafe Labs perform form an attacker's perspective?
Related tools
Recommended
Script.it ✓
FreemiumDescribe it in English, automate it instantly.
ChatGPT ✓
FreemiumAsk anything, create anything, and move from idea to action.
freebeat AI ✓
FreemiumTurn Music & Ideas into Viral Videos In One Click
Claude ✓
FreemiumBuilding reliable, interpretable AI systems
MarketAlerts.ai ✓
FreemiumInvest smarter with AI on your side
Ideamap - Brainstorm and Mindmap AI ✓
FreemiumBoost your creativity with AI-powered brainstorming.