

AI Code Security by Endorlabs ✓
AI code security that catches real issues.
Verdict
A quick read before you dig into the full page.
- Best if
- AI code security that catches real issues
- Skip if
- Limited to enterprise-scale usage
- Pick this when
- Detects potential vulnerabilities
Considering ZeroPath instead? Compare side by side
Overview
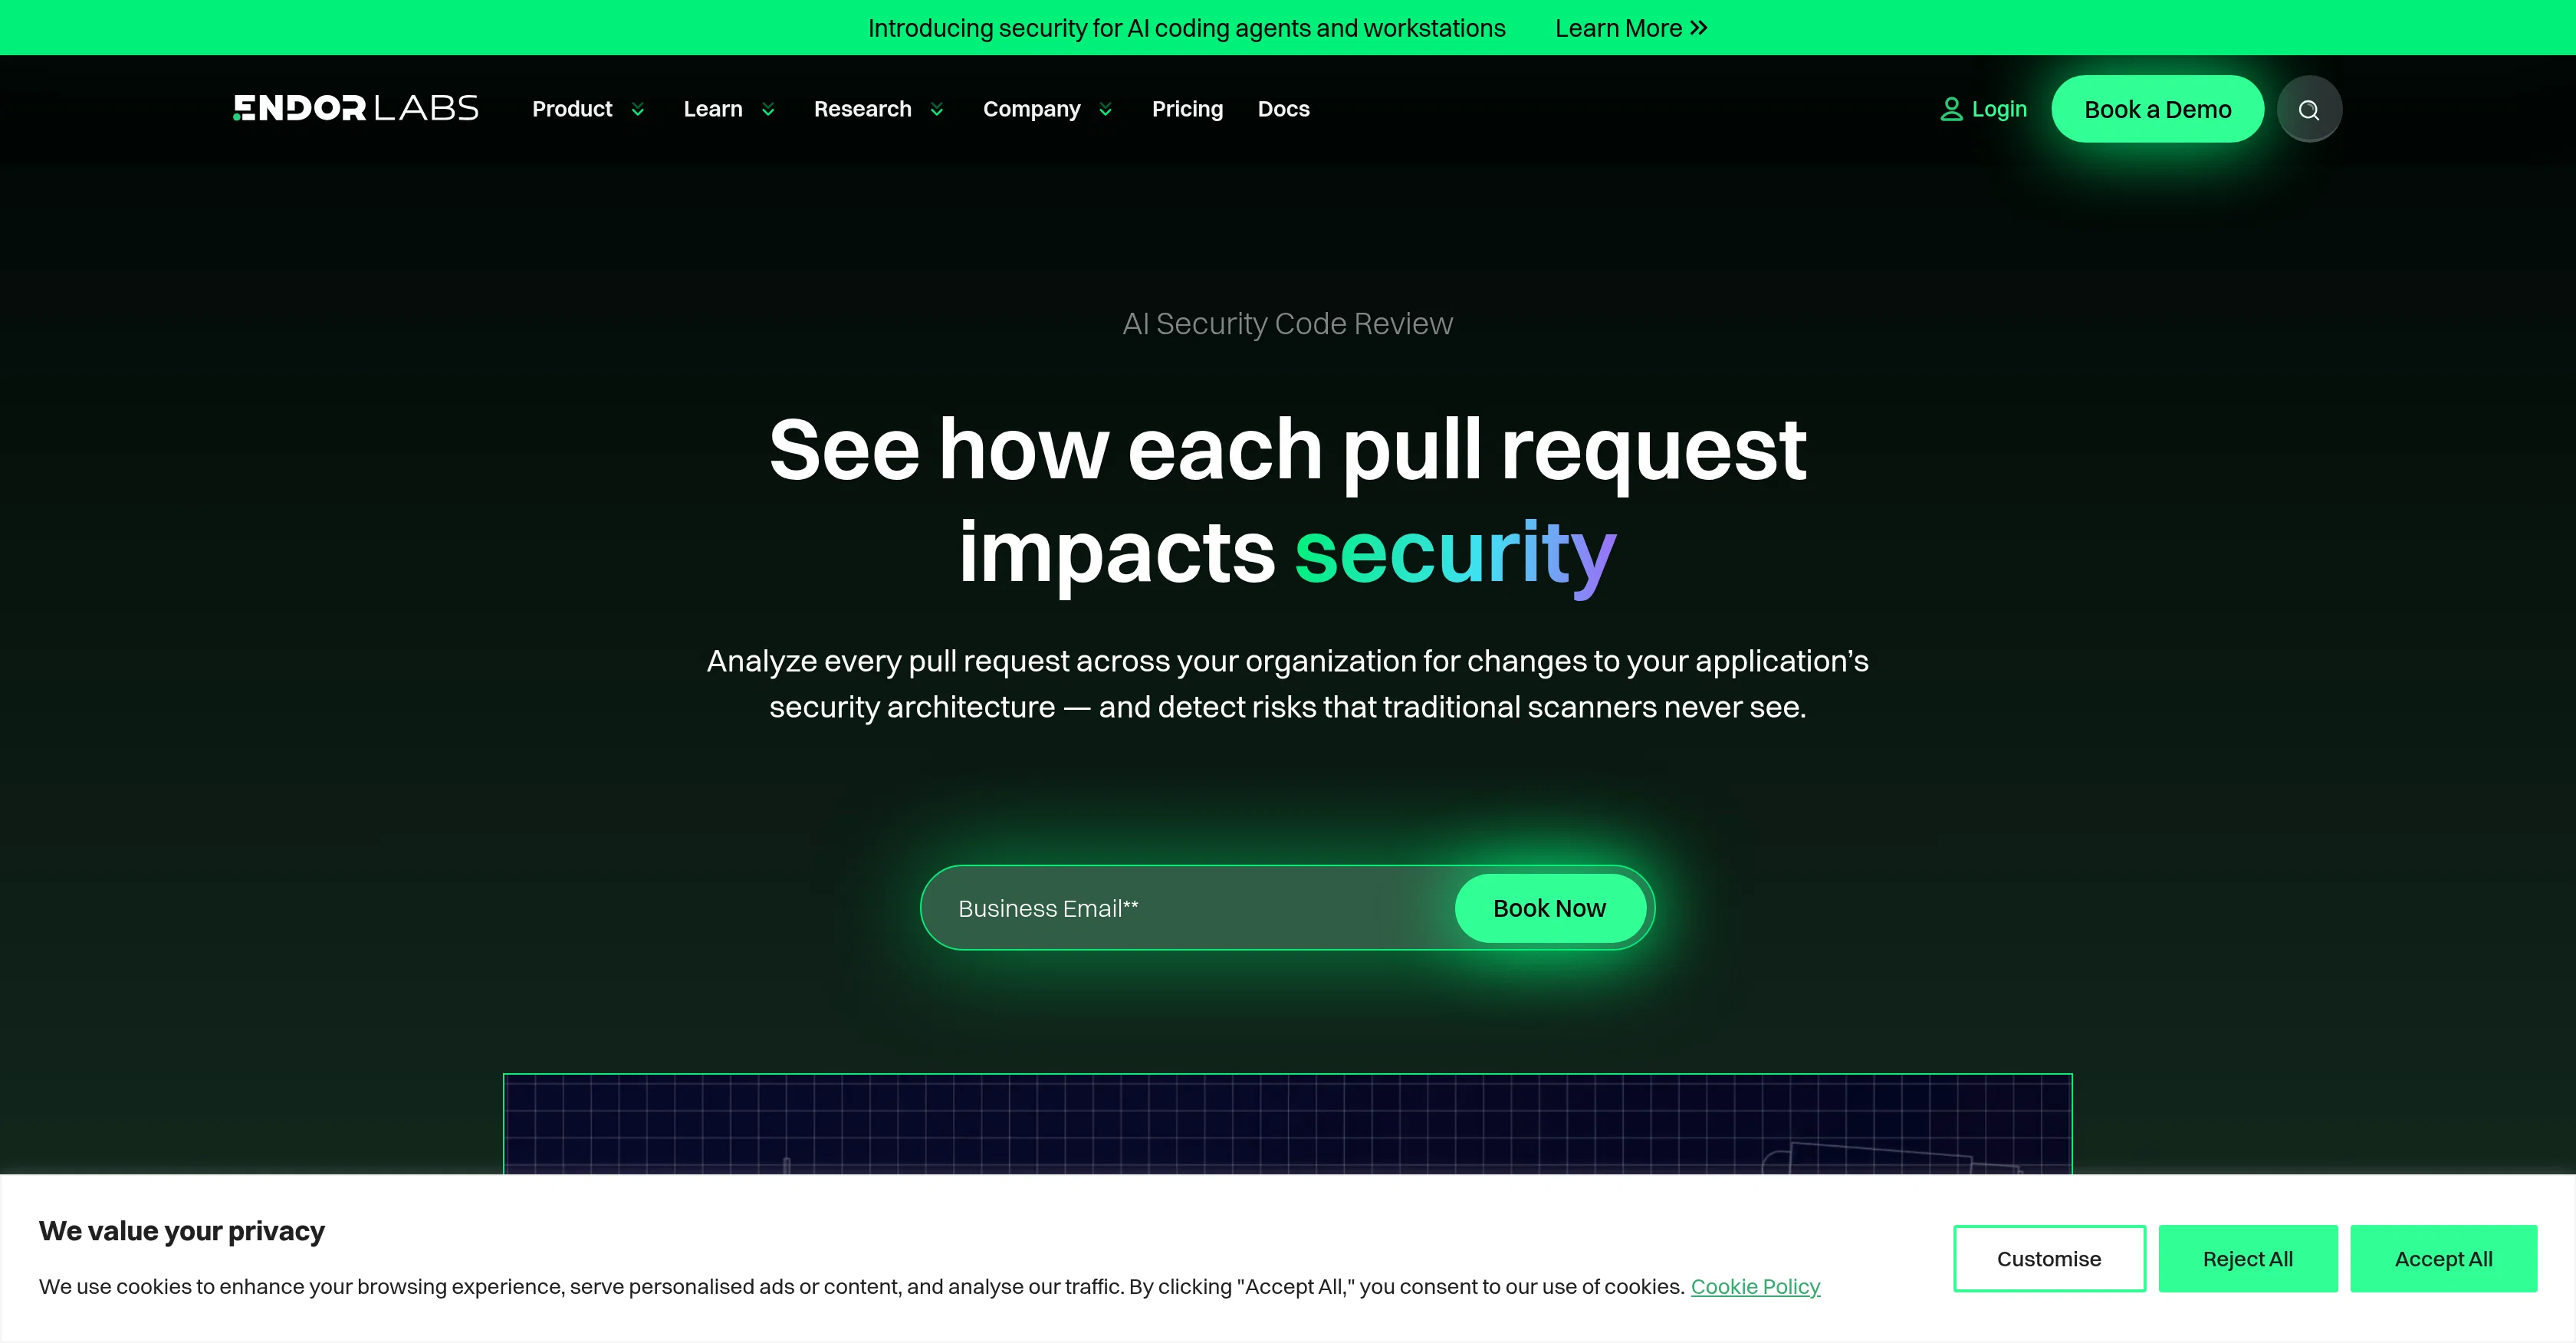
Endor Labs' AI Code Security Review is a security tool designed for reviewing AI-generated code through application security methods. It enhances code security by detecting potential risks and vulnerabilities in changes to the application's security architecture.
The tool primarily operates within a pull request environment, scanning each pull request to comprehend what changes have been made and how they could potentially impact security.
It provides context about the changes so users can quickly understand the implications of the alterations made in the code. Furthermore, it also offers the possibility to act on findings, by enabling the routings of changes to the appropriate stakeholders for quick review and resolution.
The service stands out for its capability to scrutinize every pull request for changes to the applications security architecture and establish risks that traditional scanners might overlook.
This tool is used by several major companies for both human and AI-generated code. Its objective is to identify important modifications, detect changes to critical elements such as authentication and authorization flows, cryptographic algorithms, and usage, database schemas introducing new PII collection, and payment processing logic and configurations, providing a clear, actionable context to comprehend what changed and why.
Access & connections
Where you can use AI Code Security by Endorlabs.
Platforms
Capabilities
What this tool accepts, produces, and is strongest at.
Input
- Code
Output
- Text
Supported features
- Code Review
Pros & cons
Pros
- Detects potential vulnerabilities
- Analyzes pull requests
- Contextual understanding of changes
- Routing changes to stakeholders
- Distinguishes application security architecture changes
- Detects overlooked risks
- Identifies critical security element changes
- Clear actionable insights
Show 22 more
- Reduces noise in reviews
- Speeds up issue remediation
- Securing major companies' codebases
- Detects changes to cryptographic algorithms
- Tracks new PII collection
- Analyzes payment processing configurations
- Follow up directly with authors
- Share findings in pull requests
- Automate workflows via policies and API
- Efficient codebase scalability
- Change summarization in natural language
- Possibility to ask follow-up questions
- Detects business logic risks
- Prioritizes shifts by impact and confidence
- Ability to explore logic and design in-depth
- Contextual sharing of insights
- Tracks changes to authentication and authorization flows
- Tracks infrastructure configuration
- Detects session management issues
- Detects third-party library integration risks
- Plain language pull request summaries
- Understands intent behind changes
Cons
- Designed for pull requests only
- No real-time scanning feature
- Limited to application's security architecture
- Inability to scrutinize individual commits
- Lacks universal integration compatibility
- Could route findings inaccurately
- Dependent on stakeholders for resolutions
- May require manual code review
Show 2 more
- Doesn't support all programming languages
- Limited to enterprise-scale usage
Compare alternatives
Similar tools in the catalog — with a clear reason to open each one.

ZeroPath ✓
FreemiumAI-native SAST finding 2x more vulnerabilities with fewer false positives.
Why look Higher community rating
Full comparison
DryRun Security ✓
UnknownSecurity context as you code, without being a security expert.
No pricing
Full comparison

Endor Labs ✓
UnknownAI-powered application security that prioritizes real risks.
No pricing
Full comparison
Winfunc ✓
UnknownFind, triage, and patch security vulnerabilities in hours.
Why look Offers a public API
Full comparisonReleases 1
FAQ 12
What is the main function of Endor Labs' AI Code Security Review?
How does Endor Labs' AI Code Security Review detect risks and vulnerabilities in code?
Does Endor Labs' AI Code Security Review only scan for changes in AI-generated code?
What is the significance of Endor Labs' AI Code Security Review operating within a pull request environment?
How does Endor Labs' AI Code Security Review help users understand the implications of code alterations?
Can Endor Labs' AI Code Security Review detect risks that traditional scanners overlook?
How does Endor Labs' AI Code Security Review identify modifications in the application's security architecture?
Can Endor Labs' AI Code Security Review detect changes to authentication and authorization flows?
How does Endor Labs' AI Code Security Review handle cryptographic algorithm changes?
How does Endor Labs' AI Code Security Review manage changes in database schemas and new PII collection?
In what way does Endor Labs' AI Code Security Review handle payment processing logic and configurations?
What does the 'actionable context' provided by Endor Labs' AI Code Security Review include?
Related tools
Recommended
Thea ✓
FreemiumAI study tools to master material, not just memorize it.
Aiter.io | Paste a URL. Ship a Campaign That Sounds L... ✓
FreemiumAI marketing that sounds like you, not everyone else.
Lyric Remix Studio ✓
FreeAI-powered music generation, transcription, and album art
SodaMarketing ✓
PaidTurn any product URL into viral ad campaigns.
Cue ✓
FreeLearn music production by doing, not Googling.
Ai Melodia ✓
FreemiumSongs at the speed of imagination.