
Cydelphi ✓
Cut catastrophic incident response recovery time by 75%
Verdict
A quick read before you dig into the full page.
- Best if
- Cut catastrophic incident response recovery time by 75%
- Skip if
- Specific to Security Operations Centers
- Pick this when
- Cuts incident response time
Considering Dropzone Threat Hunter instead? Compare side by side
Overview
Cydelphi is an AI-powered platform developed by industry veterans who have hands-on experience in running Security Operations Centers (SOCs) and managing data breaches.
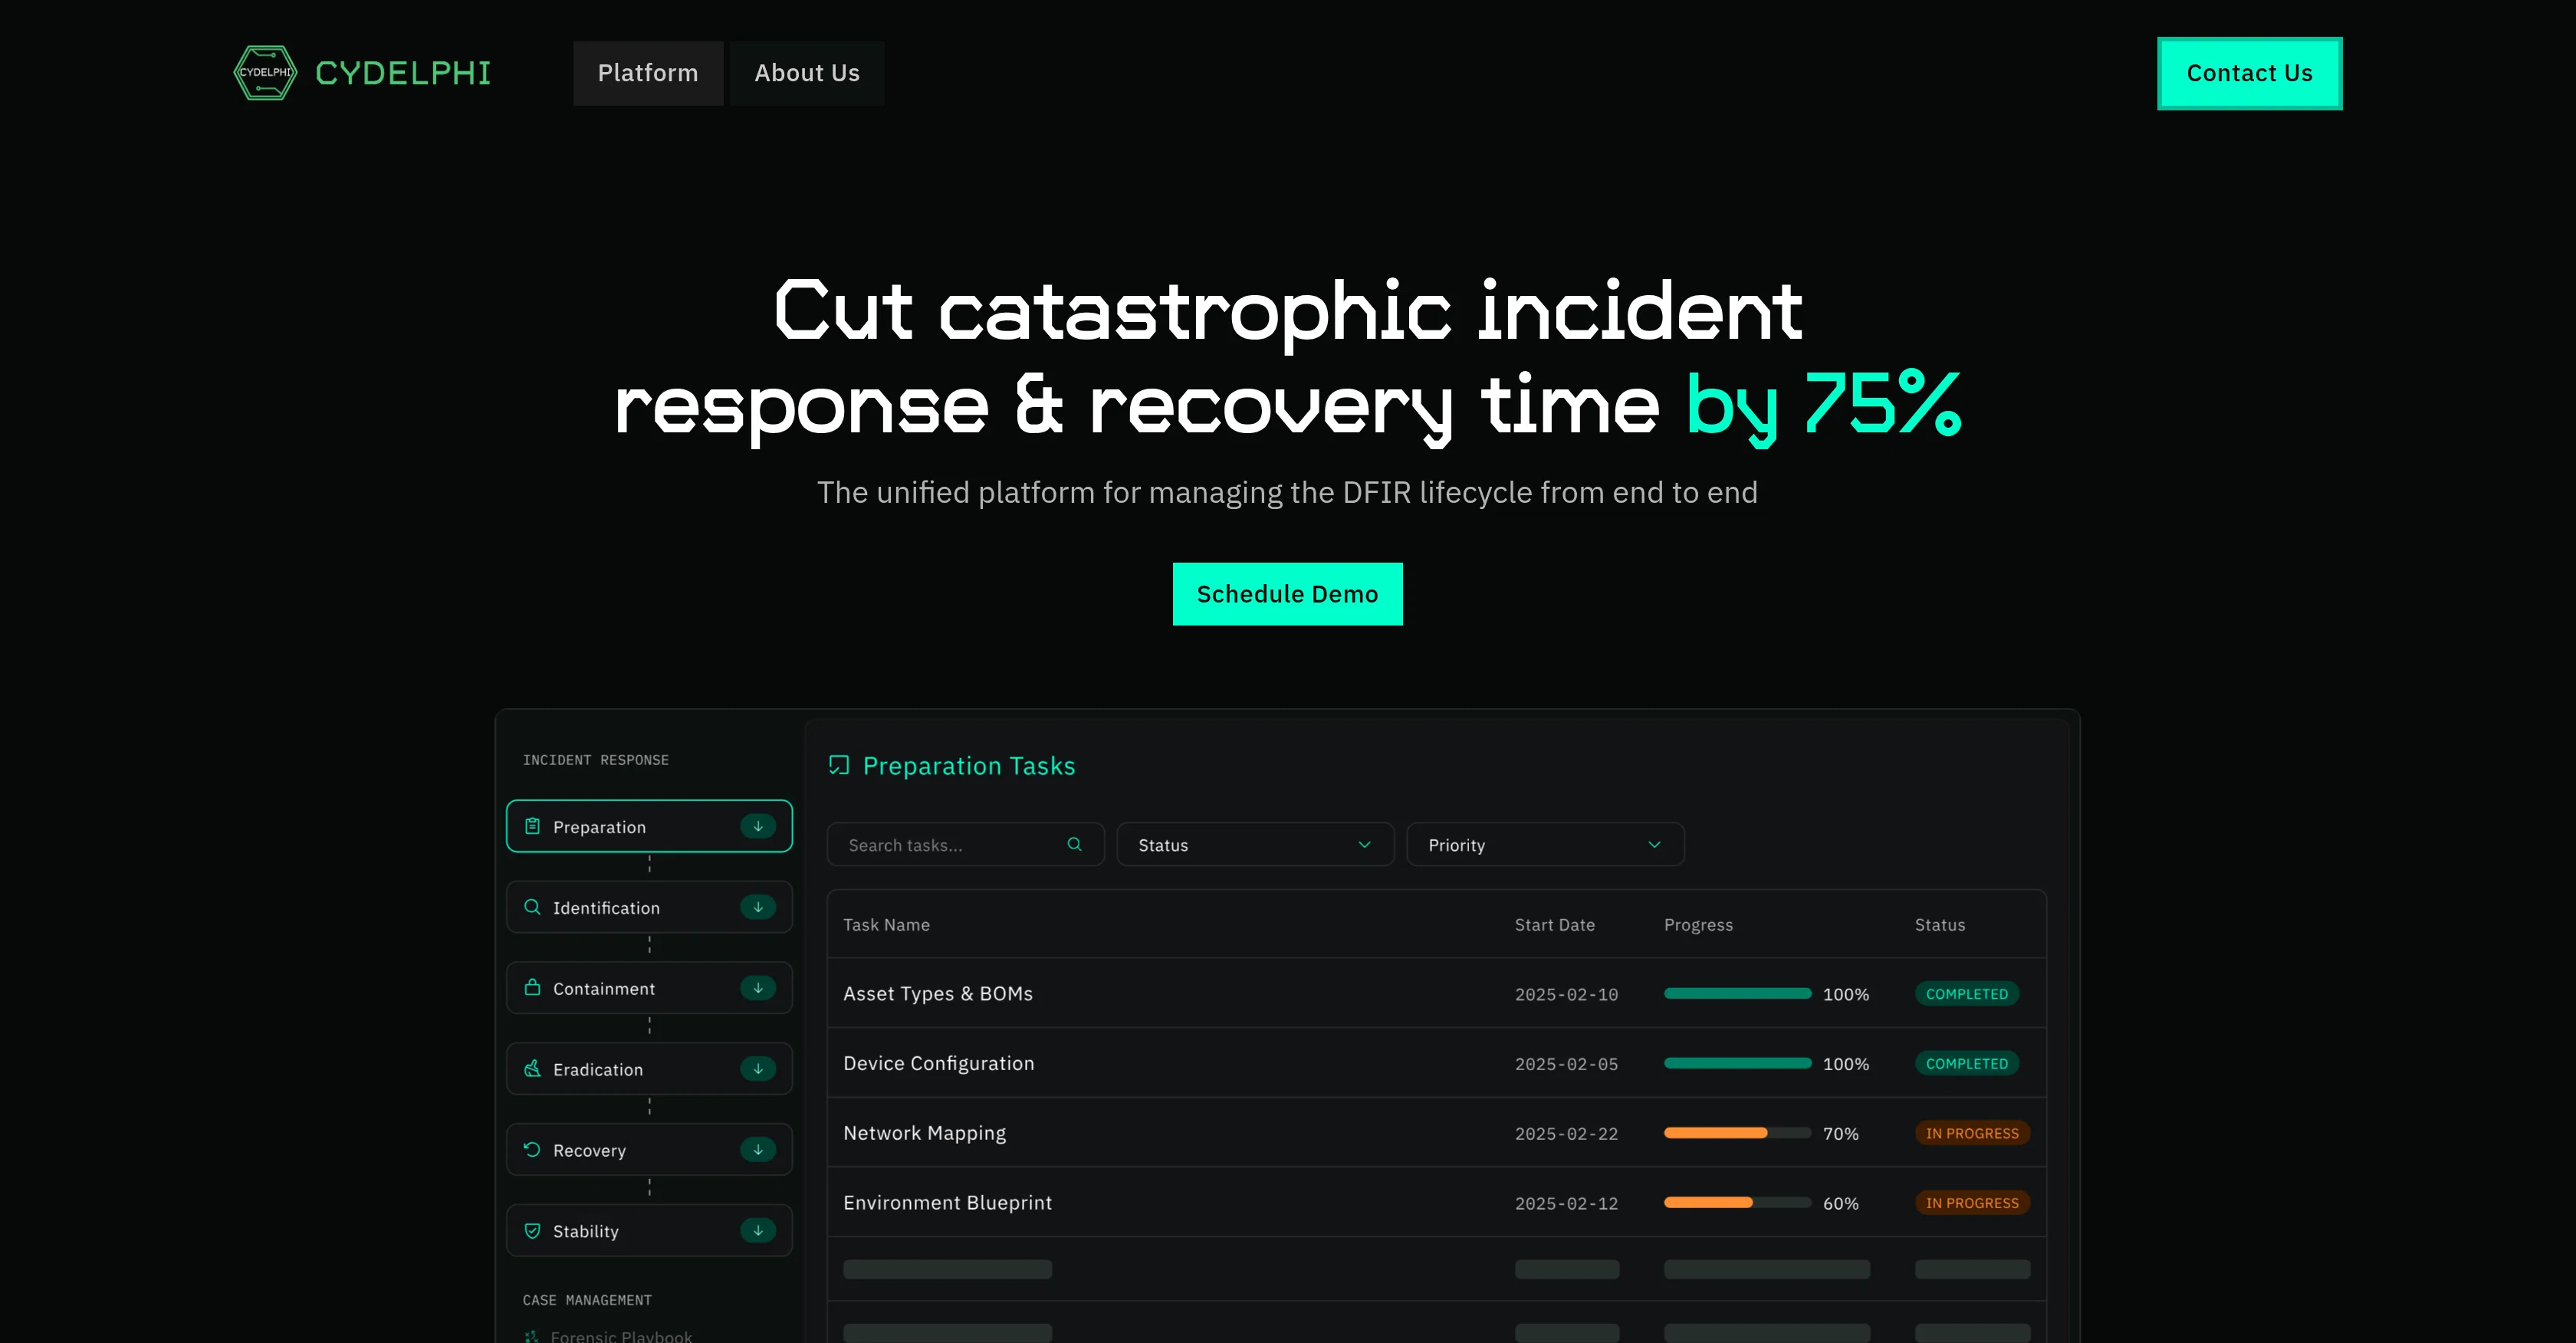
The platform is designed to significantly cut down the time required for incident response and recovery from a catastrophic data breach. It provides a unified platform that manages the entire lifecycle of Digital Forensics and Incident Response (DFIR), from preparation and identification to containment, eradication, recovery, and stability.
Cydelphi's AI-driven features include automated triage, parallel evidence gathering, systematic analysis, scope determination, as well as automated playbook execution and recovery.
The recovery method includes restoring critical systems to clean baselines while ensuring that backup providers use verified, uninfected backup points to eliminate the risk of reinfection.
The platform also feeds incident data back into the system for continuous preparation, thereby making each response faster and the system harder to compromise.
The platform provides a comprehensive solution for DFIR, offering features such as 'pre-breach vaulting' which ensures forensic informationsystem baselines, configurations, clean system imagesare always ready and available for responders.
The platform also has called 'Air-Gapped Architecture', a patent-pending technology that stores baseline configurations and recovery artifacts in a physically protected space separate from production networks.
Ransomware recovery capabilities supported by Cydelphi can achieve recovery at machine speeds. The company also provides tailored walkthroughs and demonstrations of the platform's capacities.
Enterprises, Managed Security Service Providers (MSSP), Managed Service Providers (MSP) and DFIR providers can all benefit from this platform.
Access & connections
Where you can use Cydelphi.
Platforms
Capabilities
What this tool accepts, produces, and is strongest at.
Input
- Tabular
Output
- Text
Pros & cons
Pros
- Cuts incident response time
- Automated triage
- Parallel evidence gathering
- Systematic analysis
- Automated playbook execution
- Restores critical systems
- Pre-breach vaulting
- Air-Gapped Architecture
Show 20 more
- Ransomware recovery
- Tailored walkthroughs
- 75% faster recovery
- Continuous preparation
- Scope determination
- Continuous security improvement
- Enhanced DFIR Management
- Verified backup points
- Eliminates reinfection risk
- Reduces false positives
- Detailed threat mapping
- Targeted containment actions
- Intelligent eradication plan
- Enhances Team Efficiency
- 24/7 Support
- Physical separation of data
- Patent-pending technology
- Saves on downtime
- Risk management
- Immutable system baselines
Cons
- Specific to Security Operations Centers
- No multi-lingual support mentioned
- Might lack 3rd party integrations
- Requires existing security infrastructure
- Relies on backup providers
- Lack of visibility on pricing
- No mobile application mentioned
Compare alternatives
Similar tools in the catalog — with a clear reason to open each one.



Releases 1
FAQ 12
What is Cydelphi?
Who developed Cydelphi?
How can Cydelphi reduce the time required for incident response and recovery?
What are the key features of Cydelphi?
What is the role of AI in Cydelphi?
How does Cydelphi manage Digital Forensics and Incident Response (DFIR)?
What is meant by automated triage and parallel evidence gathering in Cydelphi's features?
What's the significance of scope determination in Cydelphi?
How does Cydelphi automate playbook execution and recovery?
What does Cydelphi's recovery method entail?
How does Cydelphi handle the risk of reinfection?
What is 'pre-breach vaulting' in the context of Cydelphi?
Related tools
Recommended
OC Maker ✓
FreemiumTransform character ideas into beautiful artwork with AI.
Belin Doc ✓
FreemiumOne-click high-quality AI document translation.

Comp AI ✓
UnknownAutomate compliance for SOC 2, ISO 27001 & GDPR in weeks.
Steve ✓
UnknownAI competitive intelligence to win more B2B deals
Soniox Speech-to-Text AI ✓
FreemiumHigh-accuracy multilingual Speech-to-Text API
ChartGen ✓
FreemiumTransform data into professional charts in seconds.