

SOC 2026 Rank: #3114
Exabot Detect ✓
AI-powered threat detection with less noise.
Verdict
A quick read before you dig into the full page.
- Best if
- AI-powered threat detection with less noise
- Skip if
- Limited application ecosystem
- Pick this when
- Extensive threat detection coverage
Considering Dropzone Threat Hunter instead? Compare side by side
Overview
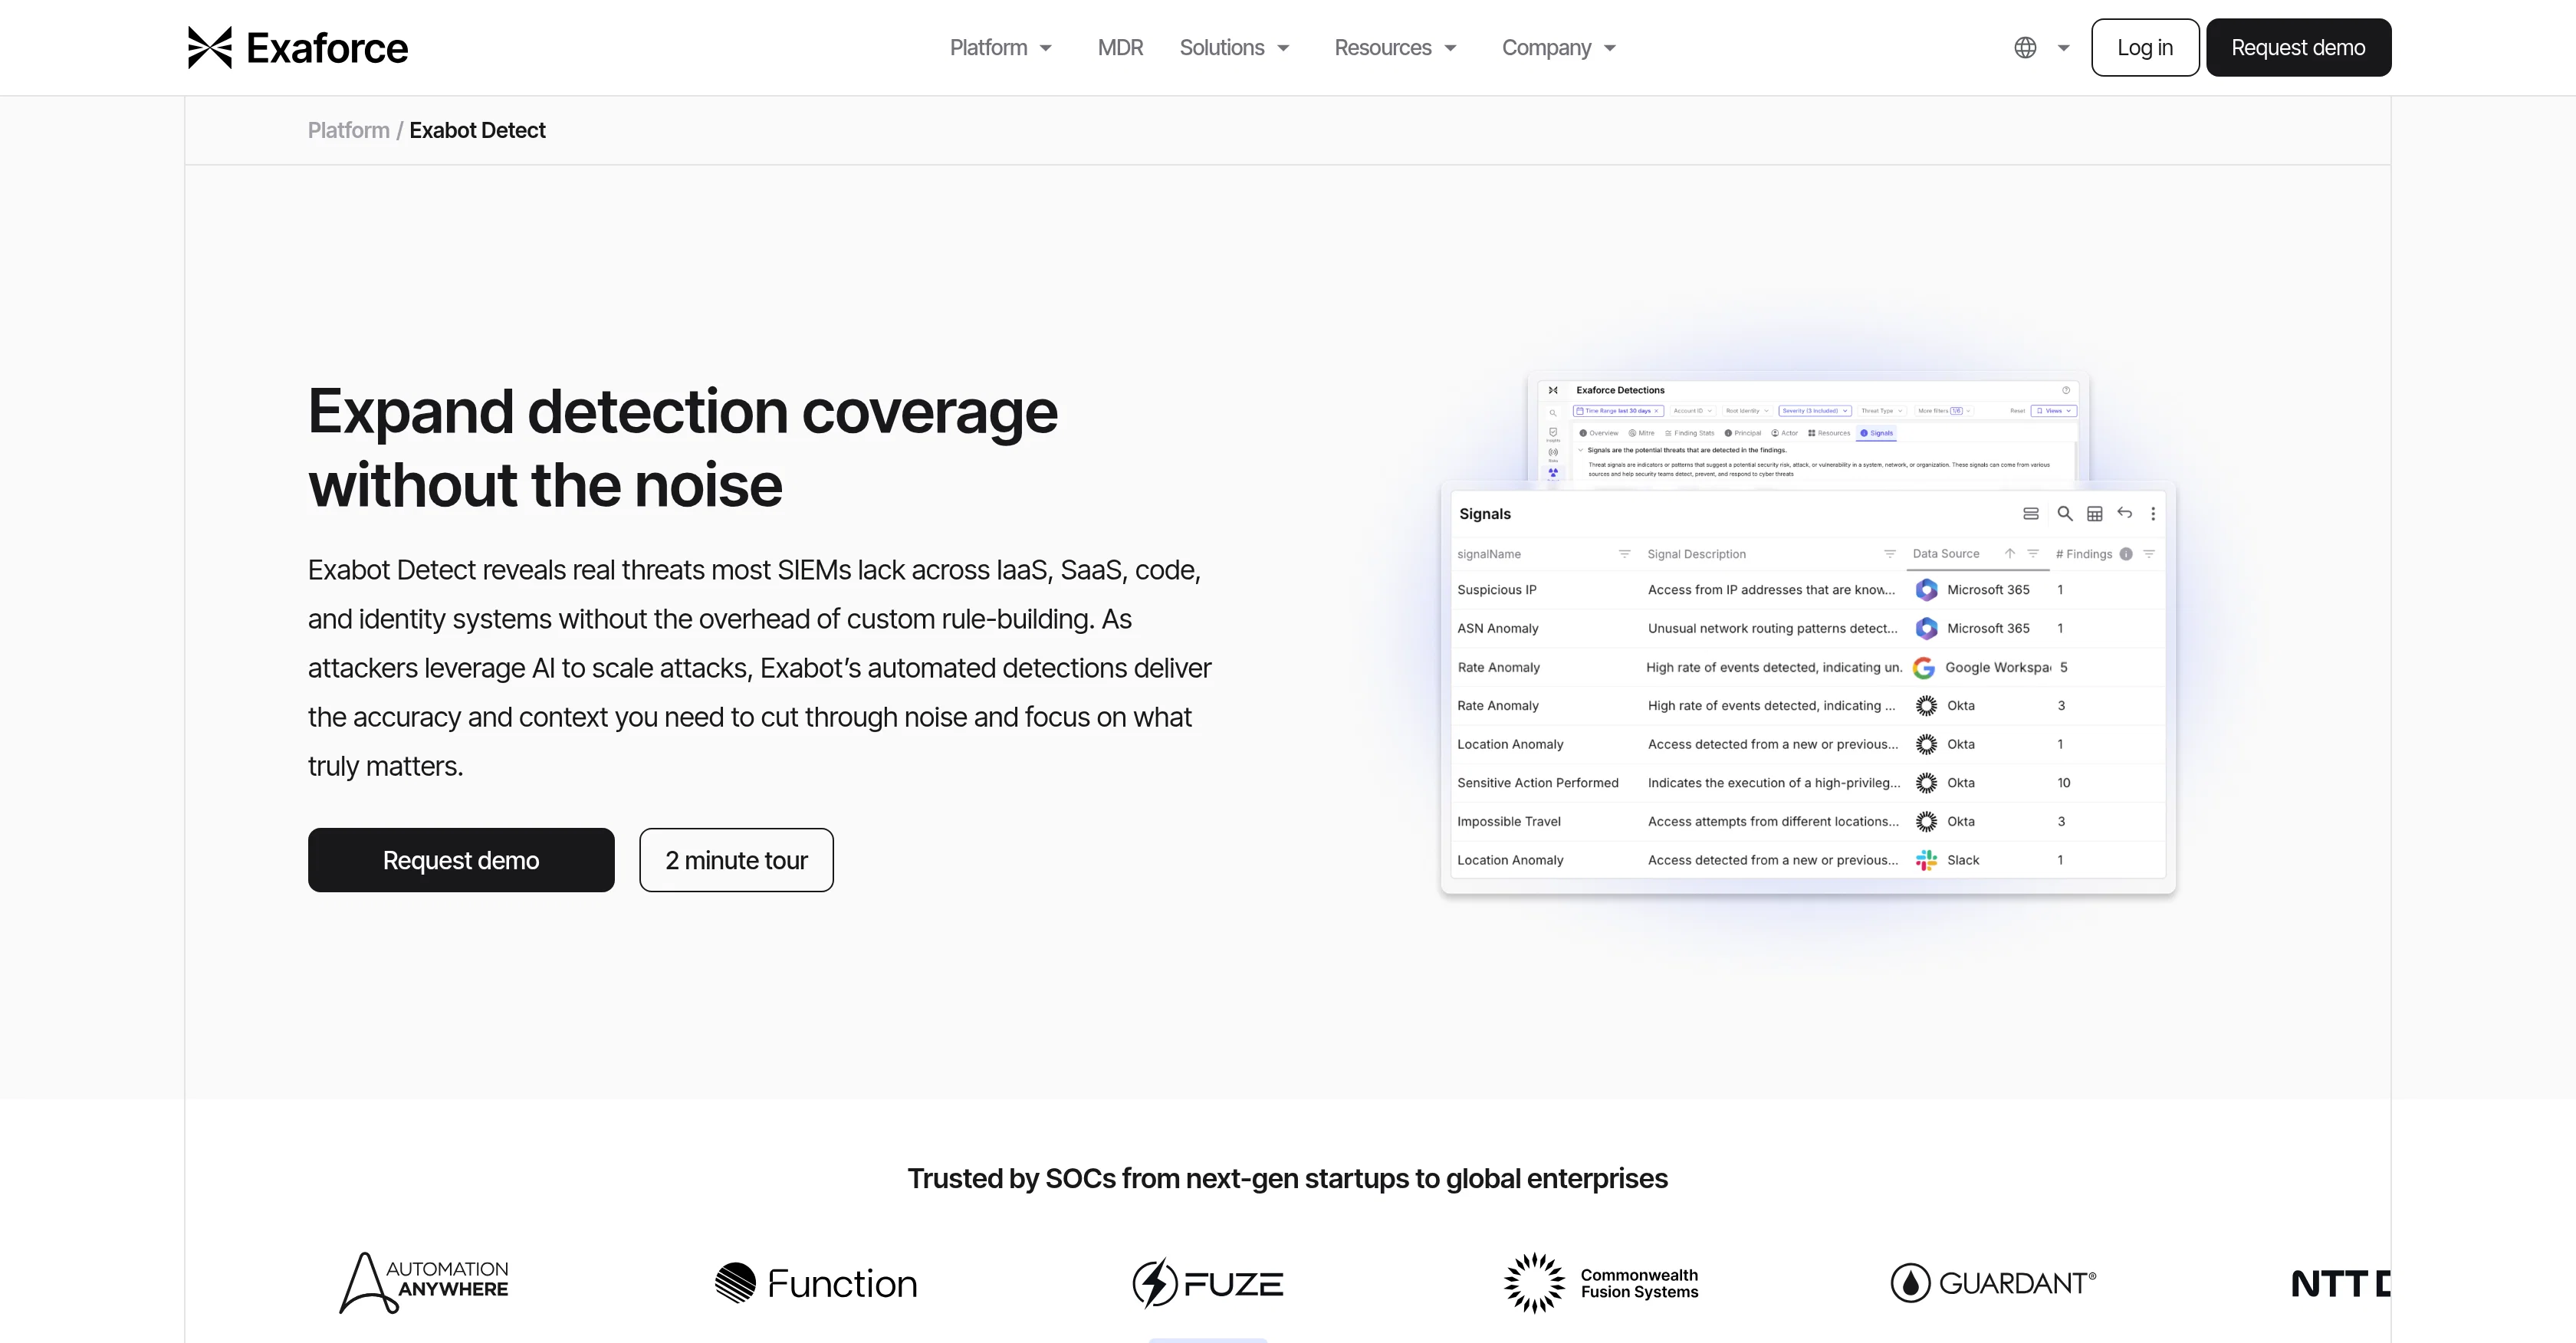
Exabot Detect, provided by Exaforce, is an AI tool that offers extensive threat detection coverage across Infrastructure as a Service (IaaS), Software as a Service (SaaS), code, artificial intelligence, and identity systems.
Aimed at improving the efficiency and accuracy of SecOps tasks, it works to surface real threats amid potential cyber noise and provides clear context for threat-related data.
This tool uses multi-model artificial intelligence engines and integrates well with various security data platforms. Exabot Detect is designed to offset the limitations of Security Information and Event Management (SIEM) systems, and aims to decrease perceived noise and blind spots.
It supports greater coverage and sharper accuracy in threat detection by using AI to keep pace with AI-driven attackers. The tool extends detection to platforms such as Google Workspace, Slack, and GitHub, providing broader visibility over such applications.
Therefore, it can help identify threats within areas of critical business activity usually missed by traditional SIEMs. One of the notable features is that every Exabot alert comes with clear, understandable, and justifiable reasoning, supported by data.
This tool can be fully managed, fully custom, or anything in between, giving the user flexible control over detection technology.
Access & connections
Where you can use Exabot Detect, and what it plugs into.
Platforms
Capabilities
What this tool accepts, produces, and is strongest at.
Input
- Tabular
Output
- Text
Highlights
- Agents
Supported features
- Cybersecurity
- Agents
- Automation
- Integrations
Pros & cons
Pros
- Extensive threat detection coverage
- Sharp accuracy
- Offsets SIEM limitations
- Decreases perceived noise
- Fills in blind spots
- Detects on Google Workspace, Slack, GitHub
- Clear, understandable alerts
- Data-supported threat reasoning
Show 35 more
- Flexible control over detection
- Security data platform integration
- Context for threat-related data
- Real-time Threat Detection
- Noise Reduction In Detection
- Detects insider threats
- Customizable tool
- Identity System Security coverage
- Less False Positive Alerts
- Higher detection rate
- Quick threat response
- Workable with varied tech-stacks
- High adaptability with varying environments
- Specific tools for SOC tasks
- Efficient FTE management
- Exaforce functionalities for legacy systems
- Efficient management of security outcomes
- Multistage detection pipeline
- High fidelity and low volume alerts
- Easy Integration with other platforms
- Wide coverage over enterprise apps
- Detects misuse and threats on SaaS
- Contextual and effective alert system
- Curated data dashboard
- Rule-based detections
- Analytical graph-based threat findings
- Auto-triage of third-party alerts
- Curated visual presentation of threat relationships
- Expansion of detection coverage without overhead
- Organisation-specific detection logic
- Reduced alert fatigue
- Secure authentication patterns
- Minimal tuning required for improvement
- Automatically triaged findings
- Constant learning and improvement of the system
Cons
- Doesn't replace traditional SIEMs
- Limited application ecosystem
- Doesn't automatically triage detections
- Relies on user feedback
- Requires manual customization
- Can't eliminate all false positives
- Doesn't specify behavioral patterns
- No explicit mention of speed
Show 2 more
- No specified data security measures
- No multilingual support
Compare alternatives
Similar tools in the catalog — with a clear reason to open each one.
Dropzone Threat Hunter ✓
PaidAutonomous threat hunting across SIEM, EDR, and cloud 24/7.
Why look Offers a public API
Full comparison
Anomali Agentic AI ✓
UnknownAI-powered visibility for security, IT, and fraud detection.
No pricing
Full comparison

Releases 1
FAQ 12
What is Exabot Detect?
What type of threats can Exabot Detect identify?
How does Exabot Detect work with SIEM systems?
What platforms does Exabot Detect support?
How does Exabot Detect help with threat detection in Google Workspace, Slack and GitHub?
What is the role of multi-model AI in Exabot Detect?
How does Exabot Detect minimize cyber noise?
Can Exabot Detect be fully managed or customized by the user?
How does Exabot Detect contribute to cybersecurity through AI?
What data does Exabot Detect use to support threat reasoning?
What is the scope of IaaS and SaaS security that Exabot Detect offers?
How does Exabot Detect handle Code Security and Identity System Security?
Related tools
Recommended
Blaze AI by Cyble ✓
UnknownReal-time AI-powered cyber threat detection and defense.

Escape.tech ✓
UnknownAI-powered pentesting that scales with your engineering.

Obsidian ✓
UnknownEnd-to-End AI and SaaS Security for Enterprises
Astelia ✓
UnknownAI reveals which vulnerabilities actually threaten you.

Salt Security ✓
UnknownSecure the APIs behind AI agents.
Oligo Security ✓
UnknownProtect AI-powered applications from real-time threats.