
AI visibility 2026 Rank: #2468
CloudByte PMS ✓
Governance, Security & Cost Tracking for AI Coding Agents
Free + from $10/mo
Verdict
A quick read before you dig into the full page.
- Best if
- Governance, Security & Cost Tracking for AI Coding Agents
- Skip if
- Limited to selected platforms
- Pick this when
- Comprehensive various metrics tracking
Considering Loamly instead? Compare side by side
Overview
AI agents now write the majority of new code in AI-forward teams, but each tool — Claude Code, Cursor, GitHub Copilot — ships its own console, logs, and billing. Nothing rolls up, and the people accountable for the output are the last to see it.
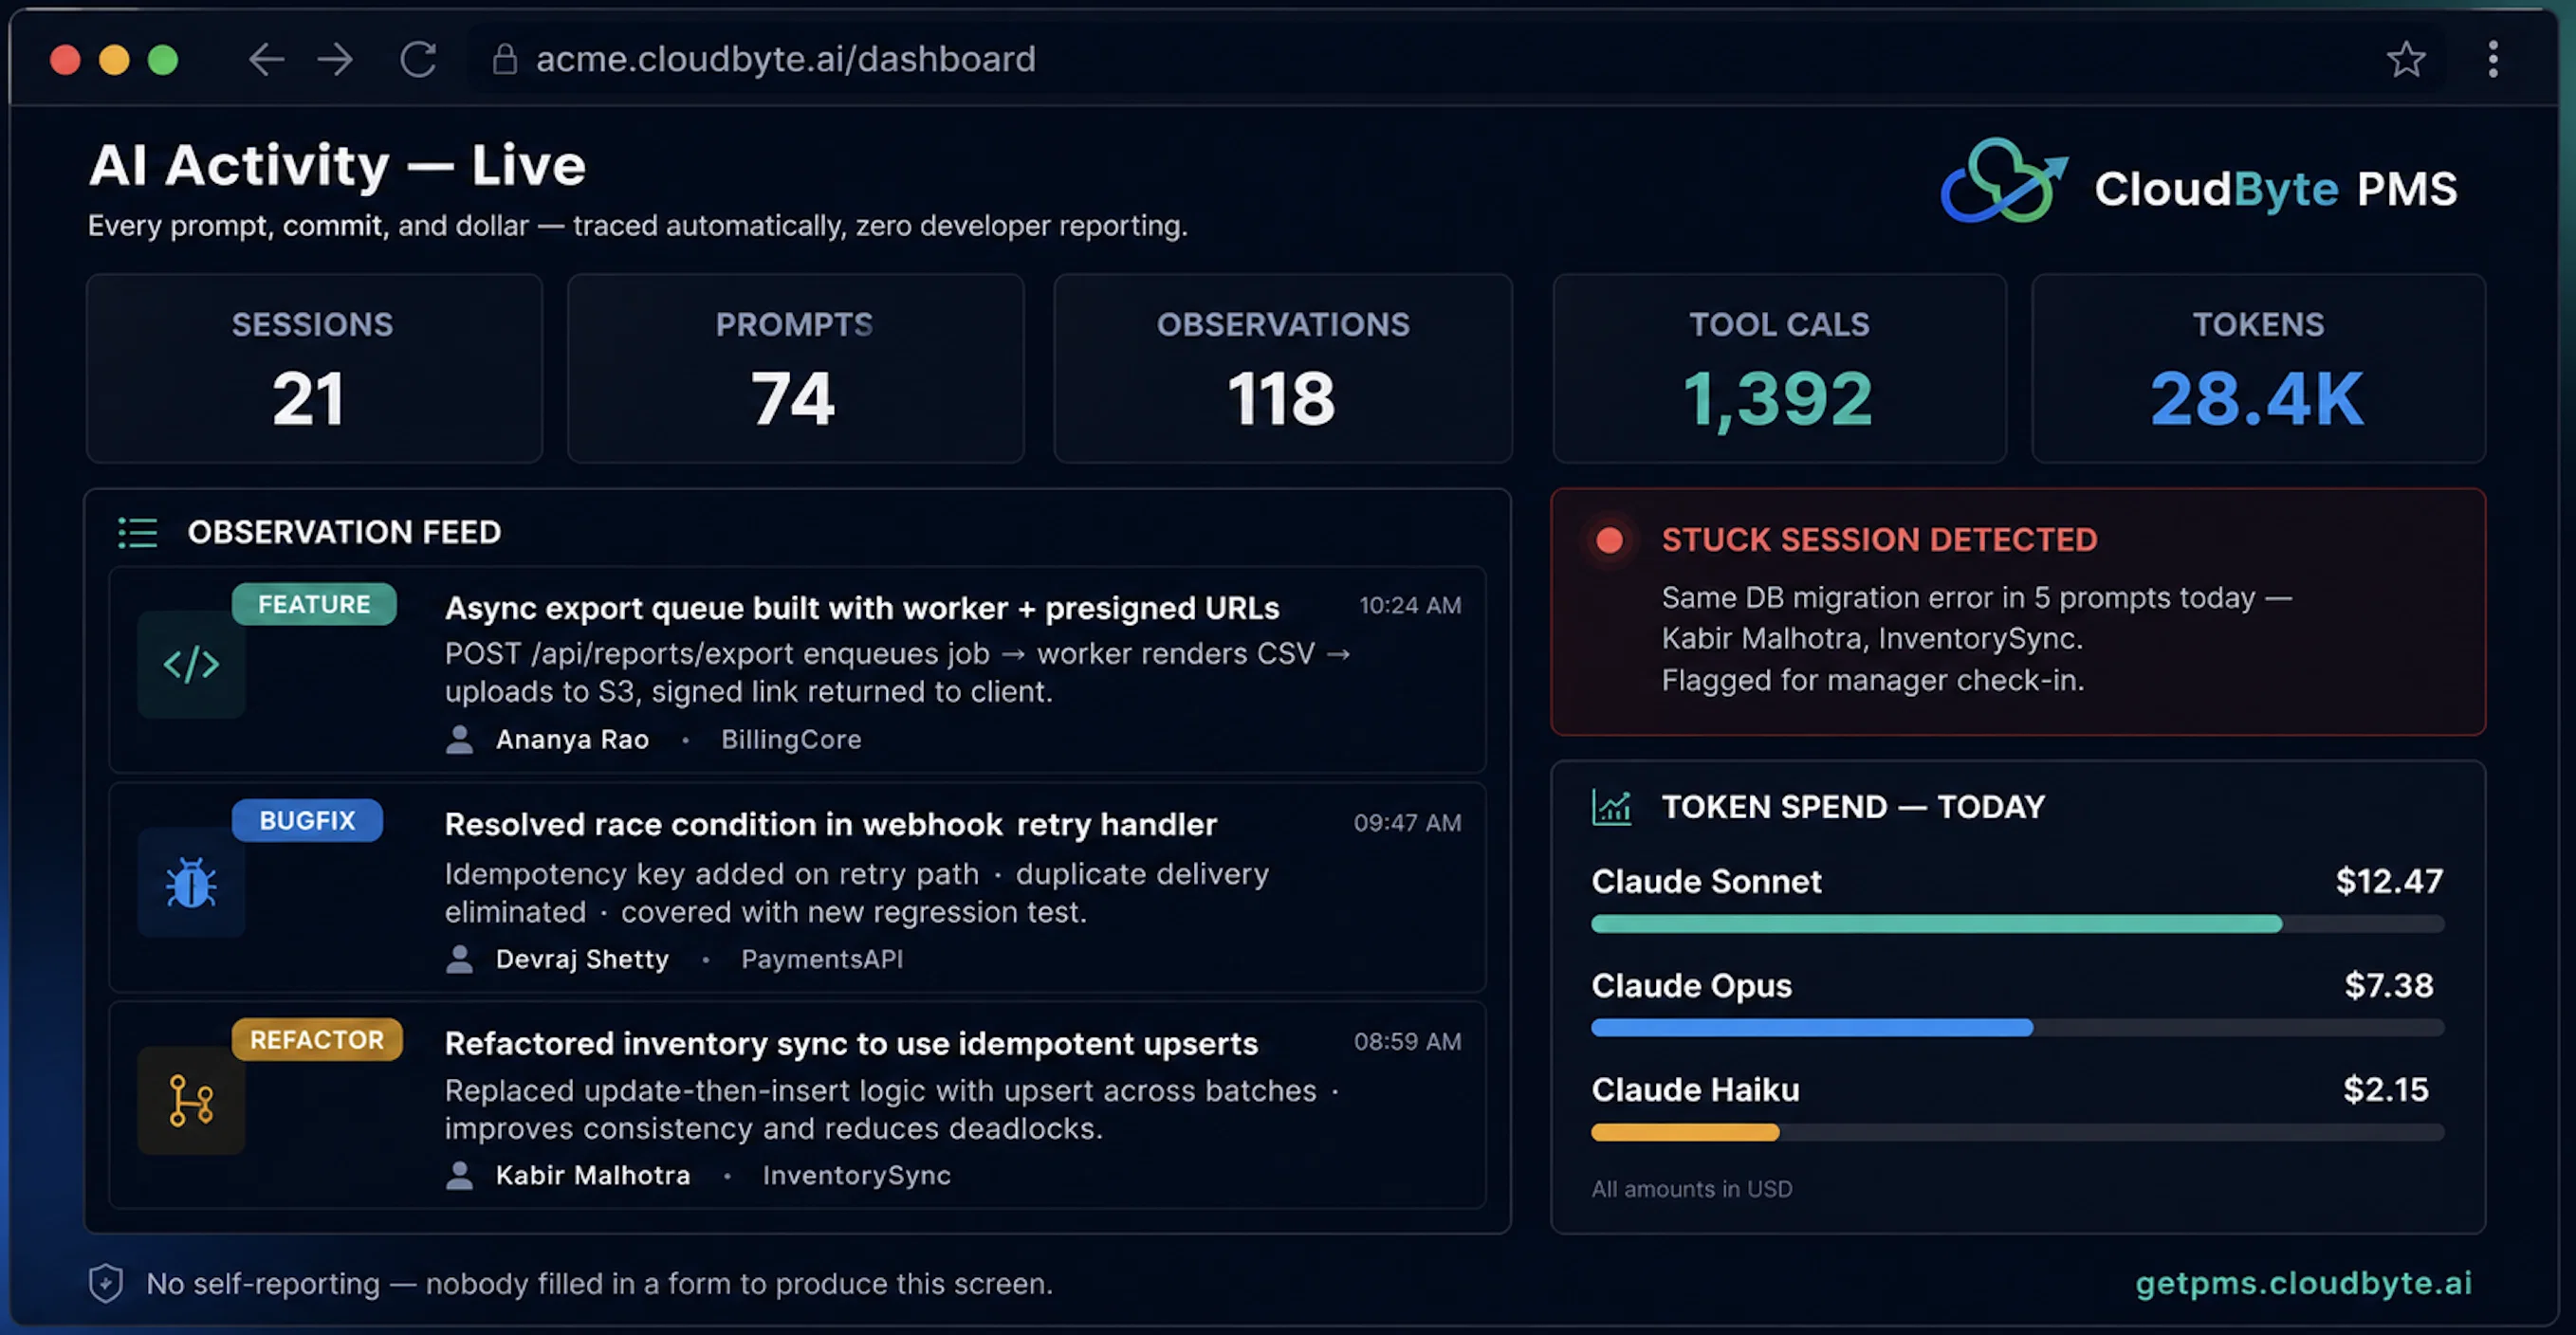
CloudByte PMS fixes that with a lightweight background agent that installs in under 15 minutes and captures everything automatically — zero developer reporting required. Every prompt, tool call, commit, and token is classified and correlated into a single trace: prompt → reasoning → commit → deploy.
What you get:
Execution visibility — real-time activity, stuck-session detection, DORA metrics, drill-down from a headline to the exact prompt behind it
Cost tracking — token-level spend per developer, project, and model, with duplicate-spend detection
Governance & security — sensitive-data scanning before prompts leave the developer's machine, SOP compliance scoring, full audit trail
Knowledge capture — auto-extracted, searchable knowledge base built from real engineering work, not manual wikis
Supports Claude Code, Cursor, GitHub Copilot, and more, with Jira and Git integration. Free for teams up to 5 developers; paid plans for growing and enterprise orgs.
Access & connections
Where you can use CloudByte PMS, and what it plugs into.
Platforms
Capabilities
What this tool accepts, produces, and is strongest at.
Input
- API
- Text
Output
- Tabular
- API
Pros & cons
Pros
- Comprehensive various metrics tracking
- Seamless workflow integration
- Operational within 10 minutes
- No workflow change required
- Supports multiple platforms
- Captures every developer signal
- Real-time tracking of ROI
- Prompt pattern clustering
Show 29 more
- Provides finance-friendly forms
- Detects sensitive information
- High-grade security measures
- Google SSO security
- Magic Link OAuth 2.0 PKCE
- Role-Based Access Control
- Multi-Project Tenancy
- Tracks token spend per project
- Works with GitHub, GitLab, Bitbucket
- Supports Linear and Jira
- Tracks commit velocity
- Session depth analysis
- Hours-saved tracking
- Access Control per role
- Analytics into developer efficiency
- Visibility into project efficiency
- Process efficiency estimation
- Developer activity and adoption heatmap
- In-built Proof of adoption
- Zero workflow change setup
- Automatic session, commit, prompt tracking
- Live real-time updates
- Simplified expenditure and ROI presentation
- Cross-team data isolation
- Domain-restricted access
- Automatic sensitive prompts flagging
- Enterprise-grade API architecture
- Automatic prompt-caching efficiency analysis
- Token spend by developer analytics
Cons
- No mobile support
- Requires constant internet connection
- Commit summaries may be inaccurate
- May mark false positives for sensitive information
- No multi-language support
- No offline mode
- Limited to selected platforms
- No custom integration options
Show 2 more
- 10-minute setup could hinder productivity
- Security relies heavily on third-parties
Compare alternatives
Similar tools in the catalog — with a clear reason to open each one.
Loamly ✓
Free TrialSee the visitors ChatGPT sends you — they convert 4x
Free + from $29/mo
Full comparison
Genrank ✓
Free TrialThe AI Search Platform for marketing teams.
Why look Offers a public API
Full comparison
Lucid Engine ✓
Free TrialTrack Your AI Search Presence in Real Time
Free + from $19/mo
Full comparison
Trustable ✓
FreemiumSEO Is Dead. What's Next? Rank Higher In ChatGPT Today
Why look Offers a public API
Full comparison
Are you found by AI? ✓
FreemiumFree scan: Make AI recommend your business
Why look Offers a public API
Full comparison
Releases 1
FAQ 12
Which AI coding tools does it support?
🛠️ 1
tool
wrote:
Claude Code and Cursor today, with deep session telemetry on both. Git (local and remote), Jira, and CI signals are also connected for DORA metrics. Additional agent platforms are added on the same unified schema.
What data does it store — do you see our source code?
🛠️ 1
tool
wrote:
CloudByte PMS stores prompts, session metadata, diff summaries, and file paths — not your full repository. Data is org-isolated and encrypted, with configurable retention windows.
How long does setup take?
🛠️ 1
tool
wrote:
Under 15 minutes per developer. No code changes and no workflow changes - a lightweight sync agent installs and activity starts flowing automatically.
Is there a free plan?
🛠️ 1
tool
wrote:
Yes - free for teams up to 5 developers, with dashboard access, agent status, basic insights, and 30-day history.
Can we self-host or choose our data region?
🛠️ 1
tool
wrote:
The SaaS product runs on AWS (ap-south-1) today. Dedicated-region hosting and private/self-hosted deployment are available on the Enterprise tier. We will have a options for Bring your own Database for 50+ Licenses models.
Does it slow developers down or add reporting work?
🛠️ 1
tool
wrote:
No. Everything is captured automatically at the source - there's no manual status update, no form to fill in, no change to how developers already work.
Who is this for?
🛠️ 1
tool
wrote:
Engineering managers, CTOs, VPs of Engineering, and tech leads at teams using AI coding assistants who need visibility into usage, spend, and delivery — without micromanaging.
How do you prevent secrets or credentials from leaking into AI prompts?
🛠️ 1
tool
wrote:
A pre-send secret scanner runs on the developer's machine before any prompt reaches an AI model or a commit — catching cloud keys, payment tokens, and auth credentials before they leave. Detection is tunable across three policy levels (Minimal, Standard, Strict), including entropy-based detection for unknown services and PII scanning at the strictest tier.
What access controls are in place?
🛠️ 1
tool
wrote:
Role-based access control with four tiers - Super Admin, Org Admin, Reviewer, Standard - enforced server-side, never trusted to the client.
Do you have an audit trail for compliance/security reviews?
🛠️ 1
tool
wrote:
Yes. The full provenance trail - prompt → reasoning → commit → deploy - doubles as your AI-change audit log, built for exactly the question auditors and security teams are starting to ask: "which AI wrote this change, and from what instruction?"
What security measures does CloudByte PMS uphold?
What role-based access controls does CloudByte PMS include?
Related tools
Recommended
GetLogit ✓
FreemiumArtificial intelligence, available for everyone.
ChatGPT ✓
FreemiumAsk anything, create anything, and move from idea to action.

Notis ✓
Free TrialThe first WhatsApp assistant that runs on your ChatGPT and Claude subscriptions
freebeat AI ✓
FreemiumTurn Music & Ideas into Viral Videos In One Click
Jason AI ✓
PaidAI-powered assistant for B2B sales outreach
DeepSeek ✓
FreeUnravel the mystery of AGI with curiosity