
Cequence ✓
Integrated application and API protection in one platform.
Verdict
A quick read before you dig into the full page.
- Best if
- Integrated application and API protection in one platform
- Skip if
- Mightly be overly complex for users
- Pick this when
- Integrated application and API protection
Considering SecureSaaS instead? Compare side by side
Overview
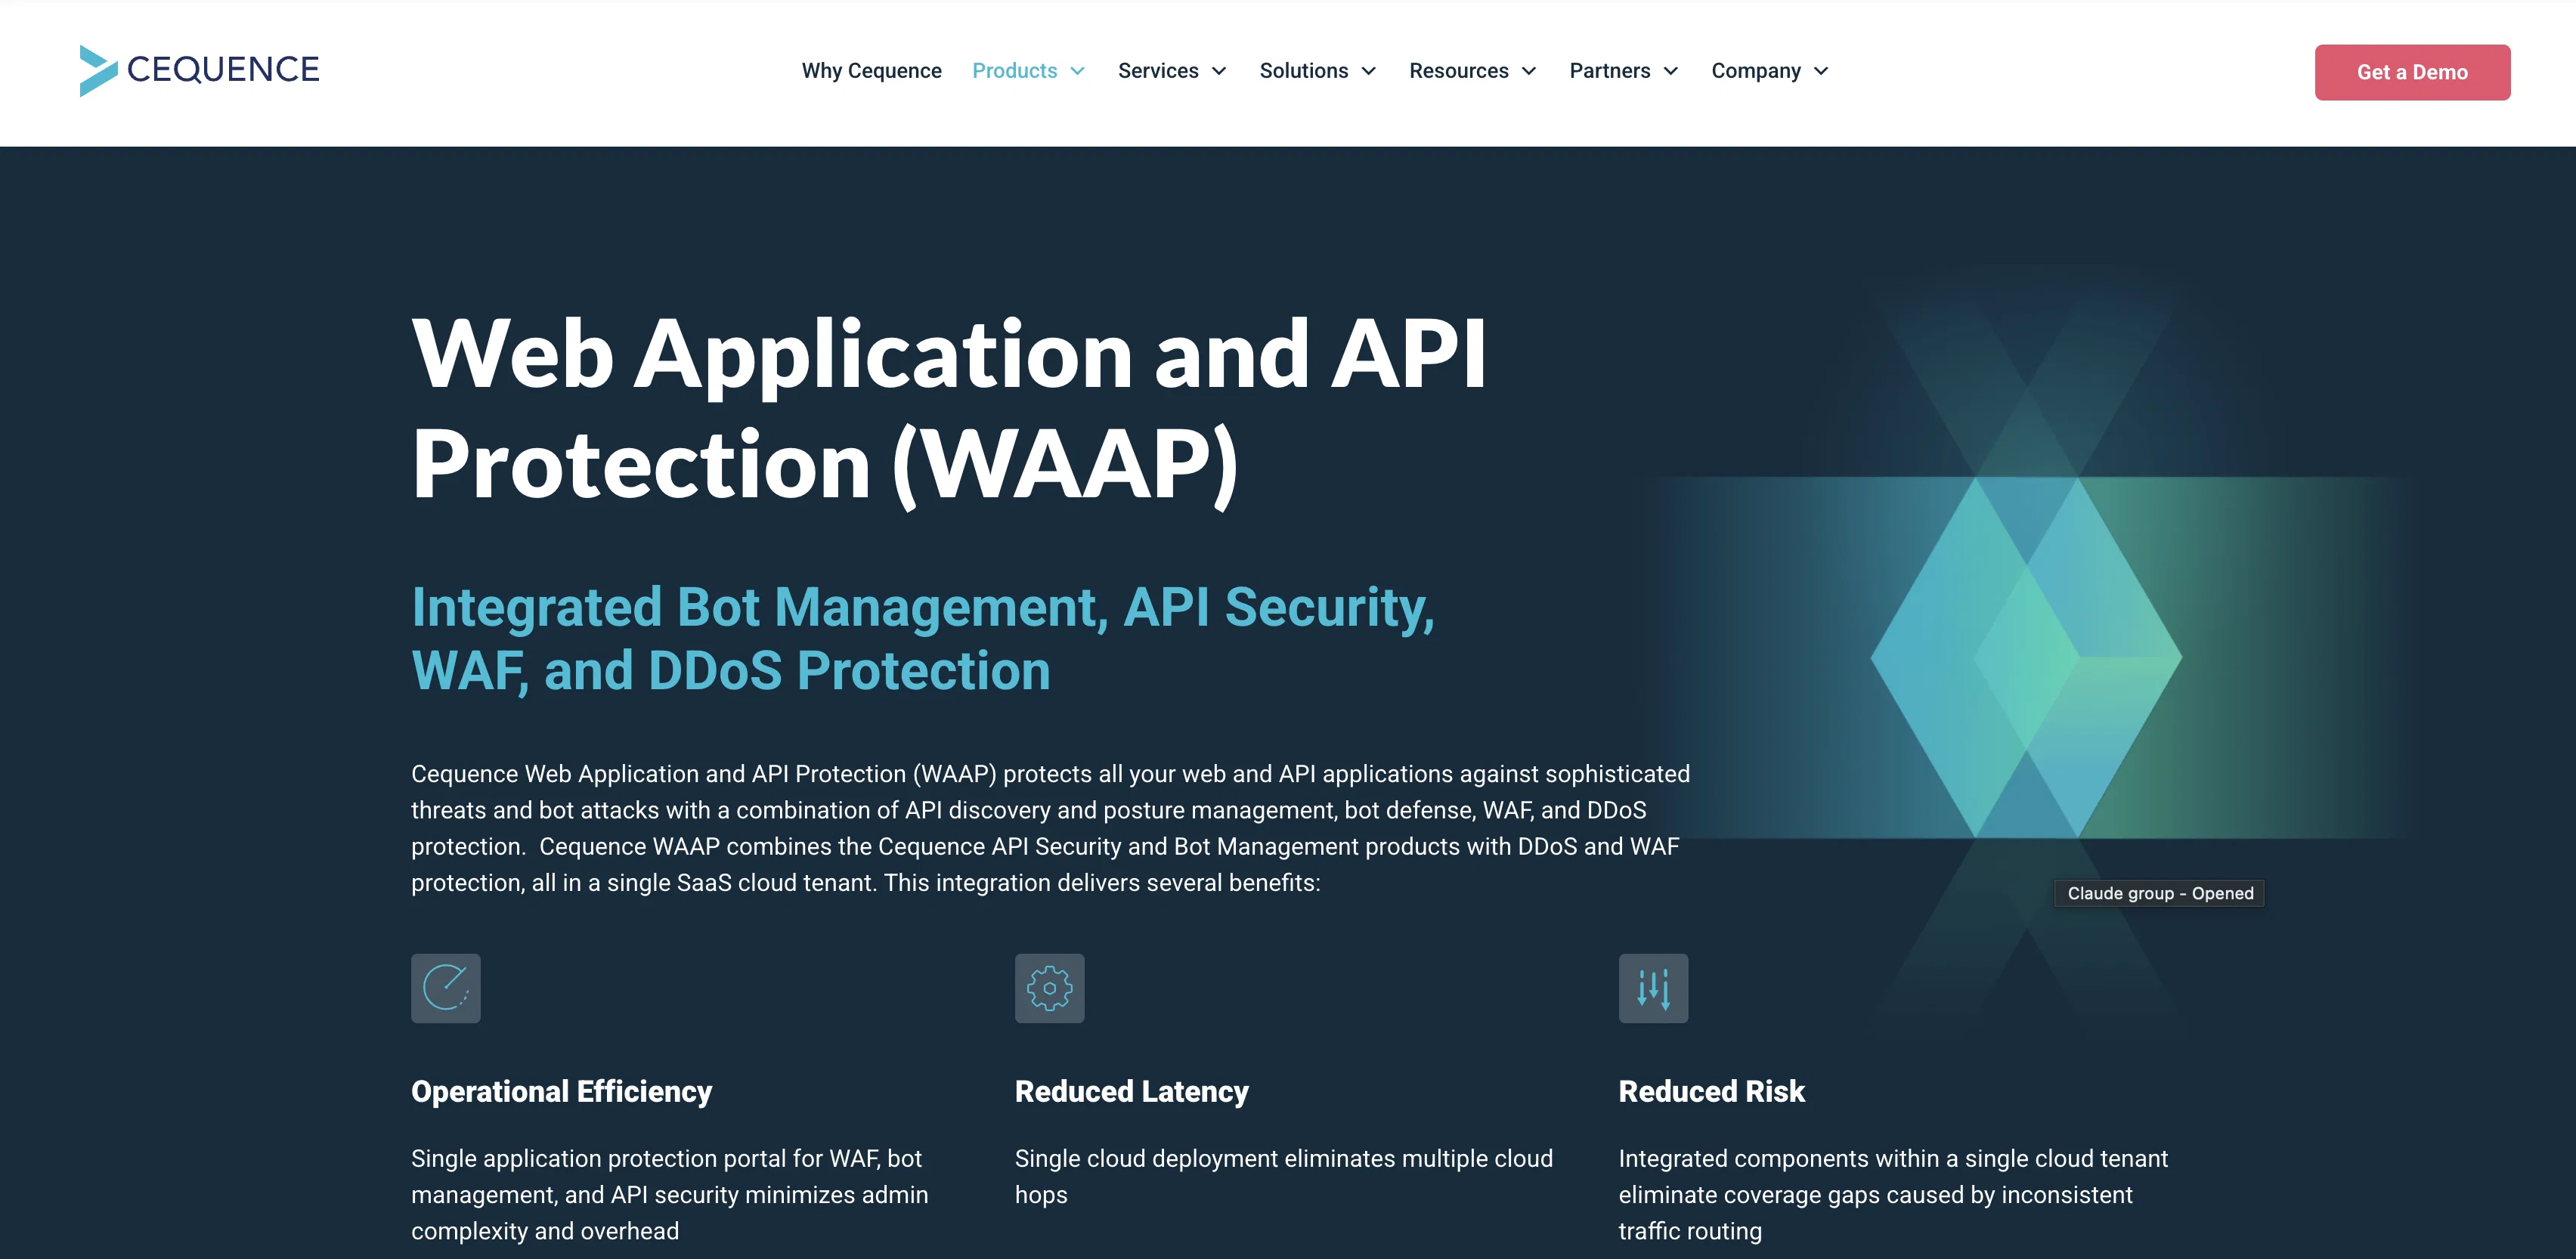
Web Application and API Protection (WAAP) by Cequence Security is a cloud-based product designed to provide integrated protection for both applications and APIs.
It is an all-in-one tool that combines aspects of bot management, API security, Web Application Firewall (WAF), and protection against Distributed Denial-of-Service (DDoS) attacks.
WAAP seeks to protect users from data loss, theft, fraud, and other damages by preventing the full range of bot attacks. With its API security feature, the tool enables the discovery, monitoring, testing of APIs and assesses a broad range of risks that can potentially lead to compliance and governance issues, data loss, and business disruption.
The built-in Web Application Firewall strengthens protection by offering a comprehensive set of rules and policies, including protection against SQL injection attacks.
DDoS protection is put in place to defend against large-scale DDoS attacks which could potentially incapacitate APIs and business operations. WAAP relies on a single cloud deployment for all its integrated components, offering several benefits such as improved operational efficiency due to a unified protection portal, reduced latency, and reduced risk due to eliminating coverage gaps caused by inconsistent traffic routing.
Access & connections
Where you can use Cequence.
Platforms
Capabilities
What this tool accepts, produces, and is strongest at.
Input
- API
Output
- API
Pros & cons
Pros
- Integrated application and API protection
- Bot attack prevention
- Built-in Web Application Firewall
- Protection against SQL injection
- DDoS protection
- Cloud-based operation
- Reduces operational inefficiencies
- Opportune for data loss prevention
Show 36 more
- Fraud prevention feature
- Real-time API monitoring
- Integrated, comprehensive security solution
- Ease API testing capabilities
- Rapid fraud response
- Elimination of coverage gaps
- Advanced bot management capabilities
- API discovery and risk assessment
- Automatic API spec generation
- Prevent sensitive data exposure
- Operational efficiency improvements
- Reduction in admin complexity
- Elimination of multiple cloud hops
- Minimal risk of inconsistent routing
- OWASP Web App Top 10 protection
- API security testing integration
- Protection against SYN floods, UDP floods
- Layer 3, 4, and 7 DDoS protection
- 99.99% availability against common infrastructure attacks
- Prevent business logic abuse
- Prevent account takeover
- Sensitive data exposure prevention
- API inventory and risk visibility
- Comprehensive API discovery and inventory
- Compliance risk visibility
- Advanced DDoS threat responsiveness
- Comprehensive set of firewall rules
- Prevents data theft via bot attacks
- Single application protection for efficiency
- Ease of security posture improvement
- Unified protection against bot attacks
- Real-time bot attack mitigation
- Customizable protection policies
- Minimized infrastructure costs
- Cequence API Management integration
- Content scraping prevention
Cons
- Requires constant cloud connection
- Potential single point failure
- Latency dependent on network
- Risk of cloud breaches
- Vendor lock-in
- Overly comprehensive for simple applications
- Updates dependent on provider
- Lack of customizable components
Show 2 more
- Limited to provided integrations
- Mightly be overly complex for users
Compare alternatives
Similar tools in the catalog — with a clear reason to open each one.
SecureSaaS ✓
FreemiumFree website vulnerability scanner for web apps.
Why look Offers a public API
Full comparison
Connector | Hostinger ✓
PaidDeploy and manage websites directly from your IDE.
Why look Offers a public API
Full comparison
AI Builder | Hostinger Horizons ✓
Free TrialBuild web apps and websites without writing any code.
Why look Offers a public API
Full comparison
Releases 1
FAQ 12
What is Cequence Web Application and API Protection (WAAP)?
Can WAAP prevent all types of bot attacks?
What is the API security feature of WAAP?
How does WAAP protect against SQL injection attacks?
How does WAAP protect against Distributed Denial-of-Service (DDoS) attacks?
How can WAAP help to improve operational efficiency?
How do Cequence Web Application and API Protection reduce latency?
What's meant by the unified protection portal in WAAP?
How does WAAP assess compliance and governance risks?
What is the function of the Web Application Firewall in WAAP?
Do I need a separate tool for Bot Management if I have WAAP?
How does the API security feature of WAAP work?
Related tools
Recommended
WebZum ✓
Free TrialSite, Google ad, and a 15-second video ad. Five minutes.
Kapient ✓
UnknownCatch hidden website errors before they cost you sales.
Website Auditor.io ✓
Free TrialDoes ChatGPT recommend your business?
Ghostwall ✓
Free TrialDetect click fraud and recover ad spend.
PACT | Free Compliance Audit ✓
Free100% Free AI-powered website compliance audits in minutes.

PageLens AI ✓
PaidAI-powered website audits with instant fixes.