
Pentesting 2026 Rank: #2639
Maced AI ✓
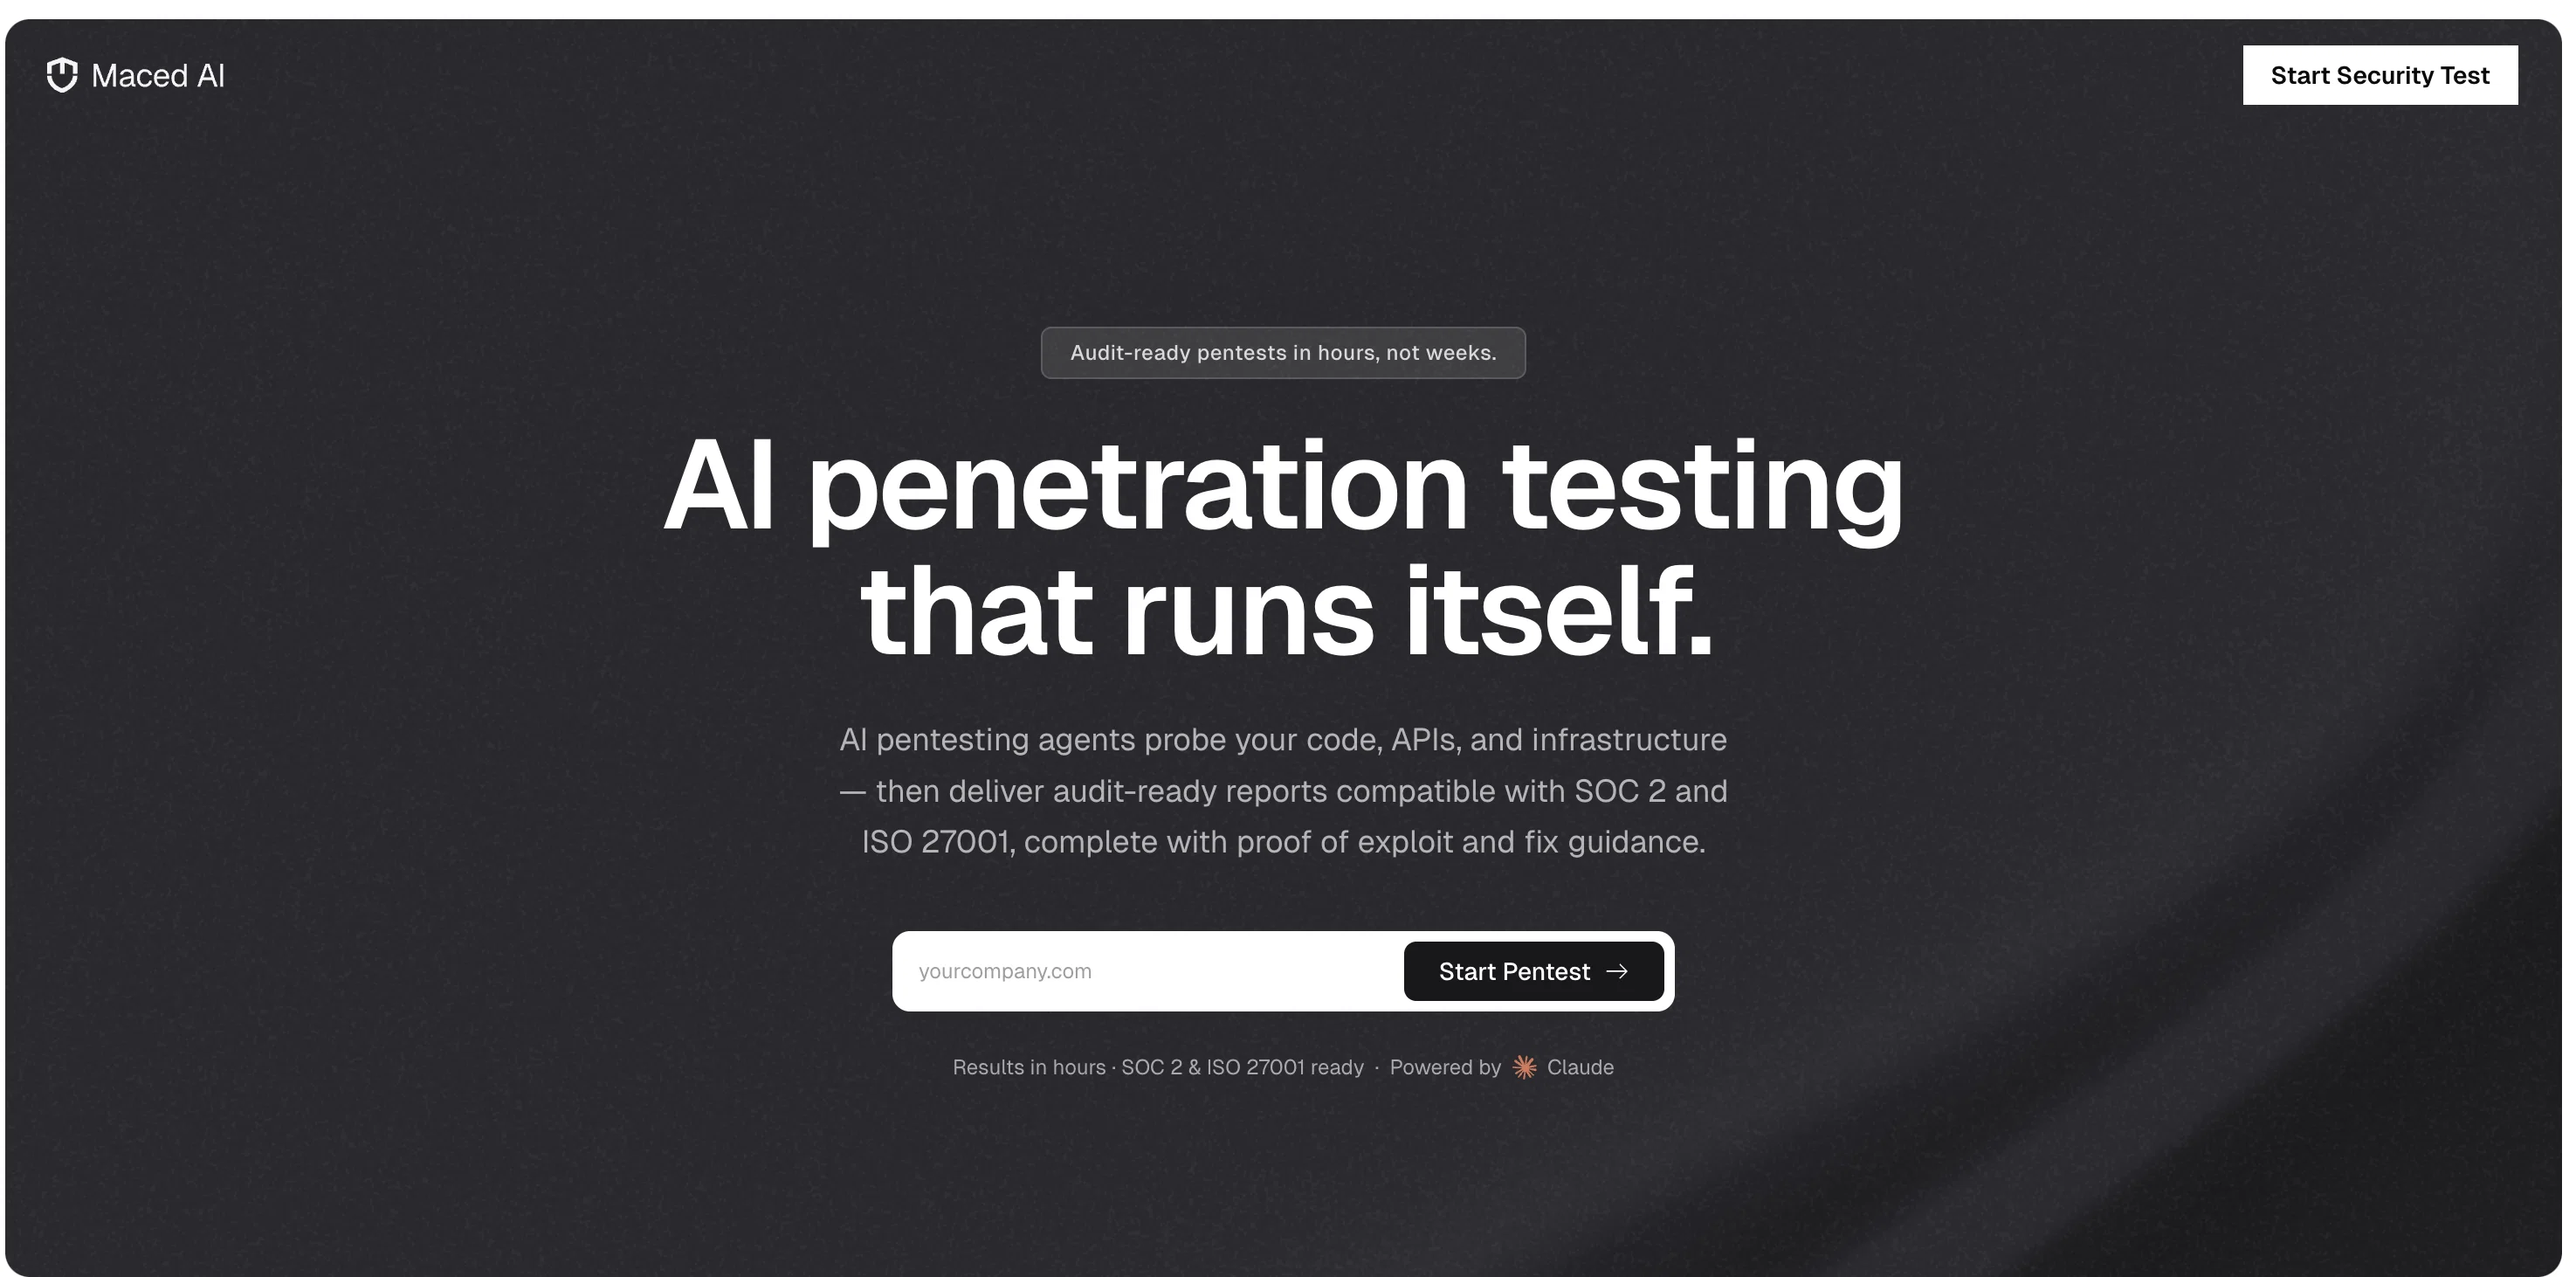
AI penetration testing that runs itself.
from $249/mo
Verdict
A quick read before you dig into the full page.
- Best if
- AI penetration testing that runs itself
- Skip if
- Limited integration options
- Pick this when
- Audit-ready reports
Considering HackerAI instead? Compare side by side
Overview
Maced AI is an autonomous AI penetration testing platform that provides audit-ready reports compatible with SOC 2 and ISO 27001. Available for both black-box and white-box testing, it encompasses a range of testing areas including code, APIs, web applications, and infrastructure.
Its AI agents probe an organization's code, APIs, and infrastructure and deliver comprehensive reports with proof of exploit and fixes. Specifically, Maced AI uses AI pentesting agents to crawl, fuzz, and exploit web applications and APIs which cover the OWASP Top 10, business logic flaws, and authentication bypasses.
It undertakes deep source code analysis of repositories for injection flaws, hardcoded secrets, insecure dependencies, and vulnerable configurations. Moreover, it tests network services and validates infrastructure hardening against real-world attack techniques.In the event of an issue, Maced offers a continuum from detection to fixing in seconds.
It ensures auto-validation of the findings, confirms exploitability with proof, and prioritizes by the real impact. In addition, auto-fixing is activated with one-click, generating a fix which is retested to confirm the vulnerability is eradicated, delivering a merge-ready PR.
Finally, Maced AI continues this process with 24/7 pentesting coverage, detecting new issues when they appear, and instantly testing latest threats and CVEs.
To maintain convenience, the platform runs pentests on a schedule that you determine, whether daily, weekly, or whenever you deploy a new product.
Access & connections
Where you can use Maced AI.
Platforms
Capabilities
What this tool accepts, produces, and is strongest at.
Input
- API
- Code
Output
- Code
- Tabular
- API
- Text
Highlights
- Agents
- API
Supported features
- Cybersecurity
- Agents
- API
- Automation
- Integrations
- SOC 2 Compliance
Pros & cons
Pros
- Audit-ready reports
- Reports with exploit proofs
- Remediation guidance
- Checks OWASP Top 10
- Detection of business logic flaws
- Authentication bypass detection
- Deep source code analysis
- Cloud security testing
Show 40 more
- Infrastructure security testing
- Network services testing
- Infrastructure hardening validation
- Real-world attack techniques testing
- Automatic issues detection
- Automatic fix generation
- Validation of any findings
- Deprioritization of any found issues
- Deduplication of issues
- Prioritization of pertinent issues
- Supports Black-box testing
- Supports White-box testing
- External attack surface testing
- Full source code review
- Continuous monitoring
- Scheduled scanning at user's preference
- Role-based access controls
- Audit logging
- Single Sign-On (SSO)
- Enterprise-grade security
- Exploit detection
- Security flaws detection
- Uncovers code injection flaws
- Hardcoded secrets discovery
- Insecure dependencies analysis
- Vulnerable configurations detection
- Threat detection
- Vulnerability remediation
- Auto-Fix feature
- Real-time threat detection
- Auto validation of findings
- Auto confirmation of exploitability
- Impact prioritization
- Continuous pentesting
- Scanning on user's schedule
- Integration with Jira, Slack, GitHub
- Custom agent tuning
- Dedicated support
- Comforms with SOC 2 standards
- Conforms with ISO 27001 standards
Cons
- Doesn't mention multiple language support
- No mobile application testing
- No explicit GDPR compliance
- Potentially high false positives
- Limited integration options
- No specified remediation validation
- Conflicting bug reports possible
- Requires source code for white-box testing
Show 1 more
- Efficiency of continuous monitoring unspecified
Compare alternatives
Similar tools in the catalog — with a clear reason to open each one.
HackerAI ✓
UnknownAI assistant that automates penetration testing workflows.
Why look Higher community rating
Full comparison
ZeroThreat.ai ✓
FreemiumFastest AI-Powered AppSec & Automated Pentesting Platform
Why look Freemium alternative
Full comparison

AISafe Labs ✓
FreemiumAI agents that assess your app with hacker expertise at machine speed.
Why look Freemium alternative
Full comparison
Releases 1
FAQ 12
What is Maced AI?
What standards is Maced AI compatible with?
How does the AI pentesting process work in Maced AI?
How does Maced AI handle OWASP Top 10, business logic flaws, and authentication bypasses?
What is included in the deep source code analysis by Maced AI?
How does Maced AI test for cloud and infrastructure security?
What is the process of detecting and fixing issues in Maced AI?
What does an audit-ready report from Maced AI include?
What are the differences between the Black-box and White-box testing modes in Maced AI?
Does Maced AI offer continuous monitoring?
Can I schedule my scans in Maced AI?
What are some of the enterprise-grade security features of Maced AI?
Related tools
Recommended
Eightify
UnknownAI-powered YouTube video summarizer extracting key ideas for quick content assessment.
Stunning ✓
PaidBuild AI-powered websites in seconds
Transcript LOL ✓
FreemiumUnlimited transcripts, summaries, 99.8% accuracy, speaker recognition, superfast
Automateed ✓
Free TrialCreate eBooks effortlessly with Automateed, the AI-powered writing tool.
Chaindesk ✓
FreemiumCustomizable chatbot for support

Limecube ✓
FreemiumTransforming the way websites are created with AI.