
Trace-AI
Predicts and prevents supply-chain attacks via metadata-driven analysis.
Source rating 5.0
(95)
232 views
232/mo traffic
0 saves
Unknown
Verdict
A quick read before you dig into the full page.
- Best if
- Predicts and prevents supply-chain attacks via metadata-driven analysis
- Pick this when
- Unknown · Free
Overview
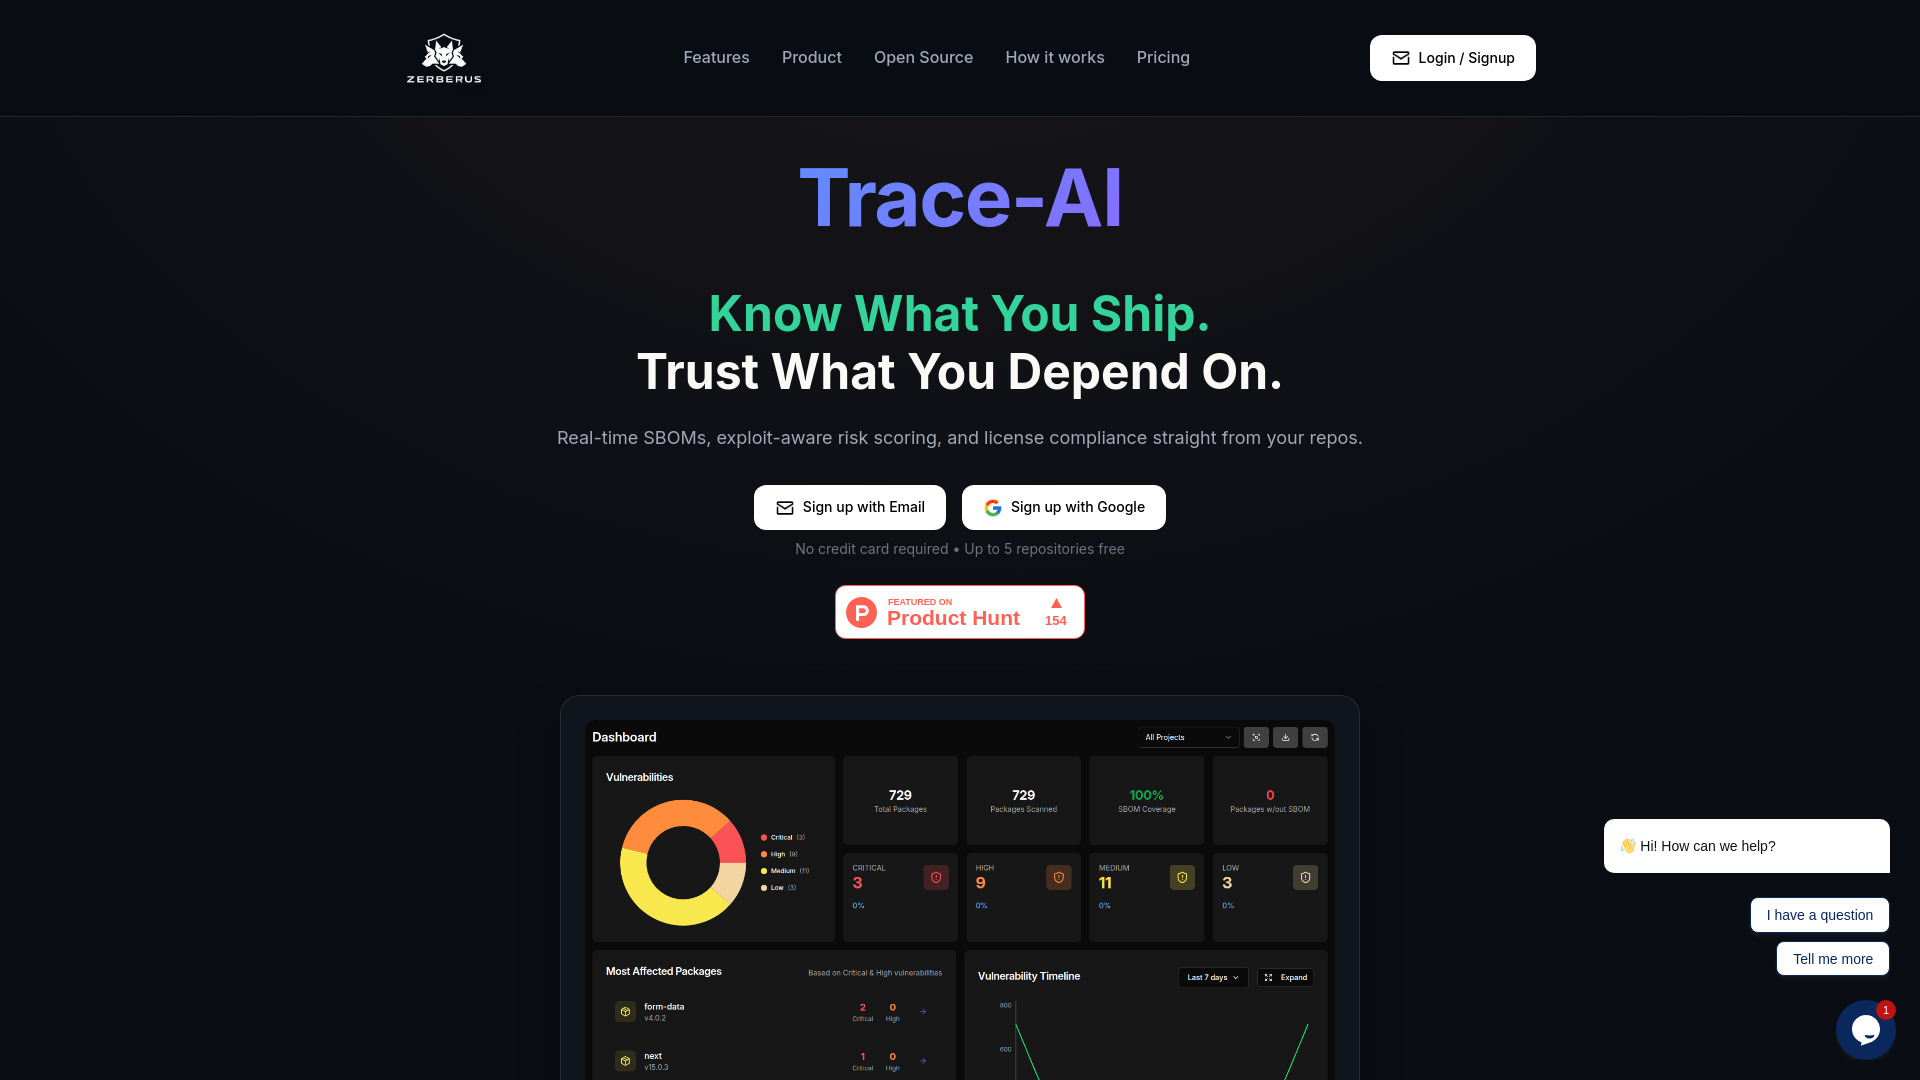
Trace-AI is a platform designed to predict and prevent supply-chain attacks. It achieves this through metadata-driven analysis of open-source dependencies, registries, and maintainer activity, without requiring access to source code. The service provides real-time Software Bill of Materials (SBOMs), exploit-aware risk scoring, license compliance, and vendor visibility. Built by experienced engineers, Trace-AI aims to help teams ship fast and securely, offering transparency through its open and auditable ZSBOM model.
Access & connections
Where you can use Trace-AI.
Platforms
Capabilities
What this tool accepts, produces, and is strongest at.
Highlights
- Real-time SBOMs (CycloneDX and SPDX)
- Exploit-aware vulnerability scanning
- License tracking and alerts
- Vendor visibility
FAQ 8
What is Trace-AI?
Trace-AI is a platform designed to predict and prevent supply-chain attacks. It achieves this through metadata-driven analysis of open-source dependencies, registries, and maintainer activity, without requiring access to source code. The service provides real-time Software Bill of Materials (SBOMs), exploit-aware risk scoring, license compliance, and vendor visibility. Built by experienced engineers, Trace-AI aims to help teams ship fast and securely, offering transparency through its open and auditable ZSBOM model.
How to use Trace-AI?
To use Trace-AI, follow these steps:
1. **Connect**: Link your GitHub or GitLab repository.
2. **Scan**: Trace-AI automatically analyzes dependencies and generates a comprehensive SBOM.
3. **Monitor**: Track vulnerabilities, exploit-aware risks, and license compliance in real-time.
4. **Export**: Generate audit-ready reports in formats like CycloneDX, SPDX, and JSON.
What is an SBOM and why do I need one?
A Software Bill of Materials (SBOM) is a complete inventory of all components in your software. It's essential for understanding your security posture, managing vulnerabilities, and meeting compliance requirements. With increasing regulatory pressure and supply-chain attacks, having an accurate, up-to-date SBOM is critical.
How is exploit-aware scanning different from traditional CVE scanning?
Traditional scanners report all CVEs, creating noise and alert fatigue. Exploit-aware scanning prioritizes vulnerabilities that have known exploits in the wild, helping you focus on real risks first. Trace-AI integrates multiple threat intelligence sources to determine exploitability.
Which programming languages and package managers do you support?
Trace-AI supports all major ecosystems including npm/yarn (JavaScript), pip (Python), Maven/Gradle (Java), Go modules, RubyGems, NuGet (.NET), Cargo (Rust), and more. Support for new package managers and languages is continuously added.
Is my code and data secure?
Yes. Trace-AI only analyzes dependency manifests and lock files – never your source code. All data is encrypted in transit and at rest. Access is limited to your dependencies file, and the workflow is metadata driven. You can also run ZSBOM locally for complete control.
How does ZSBOM compare to other SBOM tools?
ZSBOM is fully open-source and transparent. Unlike black-box commercial tools, you can audit its classification logic, customize risk scoring, and contribute improvements. Trace-AI focuses on accuracy, exploit-awareness, and developer experience.
What compliance frameworks do you support?
Trace-AI maps SBOM data to ISO 27001, SOC 2, PCI-DSS, HIPAA, and GDPR requirements. Its policy-as-code library includes pre-built compliance checks that you can fork and customize for your specific needs.
Related tools
Recommended

Trace-AI
Free