Dropzone AI ✓
Augment your SOC with AI for faster, precise threat analysis
from $36000/yr
Verdict
A quick read before you dig into the full page.
- Best if
- Augment your SOC with AI for faster, precise threat analysis
- Skip if
- Limited to cybersecurity focus
- Pick this when
- Autonomous alert investigation
Considering Judicio instead? Compare side by side
Overview
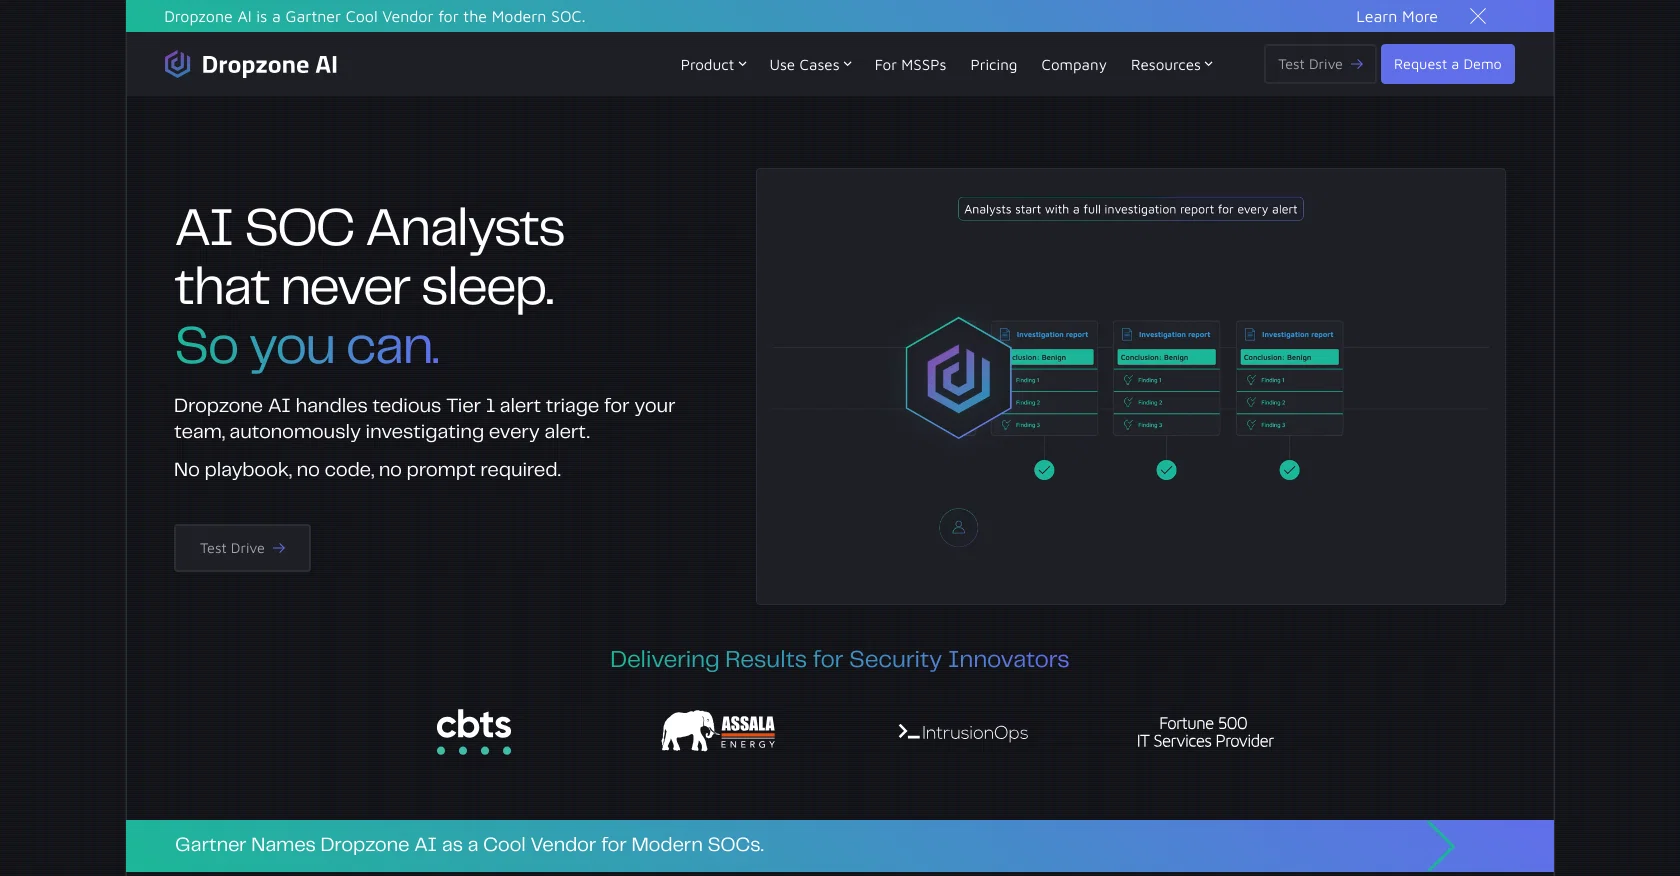
Dropzone AI is an artificial intelligence tool designed to assist with alert investigations in the realm of cybersecurity. It acts as an AI SOC Analyst, aiding security operations center (SOC) teams manage the increasing volume of security alerts.
The tool handles tasks such as Tier 1 alert triage and investigation autonomously, which eliminates the tedious manual activity, providing professionals with time to focus on more critical tasks such as policy updates, incident response planning, and threat hunting.
Its primary function is to detect real threats rapidly by identifying significant alerts worth escalating, reducing risk and the mean time to respond (MTTR).
Aside from its autonomous capabilities, Dropzone AI can adapt to specific user environments and follow given instructions, making it a versatile supplement to existing security efforts.
Furthermore, it boasts built-in integrations with multiple SOC tools, suggesting its compatibility with various security infrastructures. Users have recognized Dropzone AI for improving the speed and quality of investigations, facilitating a more efficient threat response workflow.
Access & connections
Where you can use Dropzone AI.
Platforms
Capabilities
What this tool accepts, produces, and is strongest at.
Input
- Tabular
- Text
Output
- Tabular
- Text
Pros & cons
Pros
- Autonomous alert investigation
- Eliminates manual activities
- Reduces risk
- Reduces mean time to respond
- Quick threat detection
- Handles Tier 1 alert triage
- Versatile supplement to security efforts
- Adapts to user environments
Show 26 more
- Built-in tool integrations
- Improves investigation speed
- Improves investigation quality
- Efficient threat response workflow
- Identifies significant alerts
- Uses no playbooks
- Helps with policy updates
- Facilitates threat hunting
- Increases team productivity
- Autonomous SOC capabilities
- Gartner Cool Vendor recognition
- Handles Phishing, Endpoint, Network, Cloud, Identity, Insider Threat
- Chatbot for SOC Analysts
- Identifies real threats fast
- Autonomously handles Tier 1 alert triage
- 24/7 operation
- Reduces false positives
- Single-tenant architecture
- SOC 2 Type 1 certified
- Transparent analysis
- Handles many types of security alerts
- 60+ tool integrations
- Ready to help on Day 1
- Evidence provided in chat responses
- Works alongside human analysts
- Designed for human-in-the-loop review
Cons
- Limited to cybersecurity focus
- Solely handles Tier 1 alerts
- Not a SIEM replacement
- No coding or playbook feature
- Dependent on existing SOC tools
- Emails used for analysis are deleted
- Submission emails added to mailing list
Compare alternatives
Similar tools in the catalog — with a clear reason to open each one.

Pulse by smallest.ai ✓
FreemiumWorld's fastest and most accurate speech-to-text.
Why look Freemium alternative
Full comparison
CEOfriend ✓
PaidAI-powered advisors for CEOs and founders.
Why look Typically cheaper
Full comparisonReleases 1
FAQ 12
What is Dropzone AI?
Does Dropzone AI replace SOC Analysts?
What tasks does Dropzone AI handle autonomously in cybersecurity?
How does Dropzone AI help in reducing risk in cybersecurity operations?
How does Dropzone AI aid in alert triage?
How can Dropzone AI help improve the speed and quality of investigations in cybersecurity?
How can Dropzone AI adapt to specific user environments?
What types of SOC tools can Dropzone AI integrate with?
How does Dropzone AI assist in incident response planning?
How does Dropzone AI help in threat hunting?
What does the mean time to respond (MTTR) feature of Dropzone AI imply?
How does Dropzone AI assist in policy updates in cybersecurity?
Related tools
Recommended
Ethiack ✓
FreemiumAutonomous ethical hacking to identify vulnerabilities first.
CodeThreat ✓
FreemiumCode analysis detects vulnerabilities.
Disclaimr — State compliance alerts for RIAs ✓
FreeThe SEC tells you. Fifty states don't. Disclaimr watches all of them.
Securitybulldog ✓
UnknownAI-powered cybersecurity intel to speed up remediation.

CrowdStrike ✓
UnknownStop breaches. Drive business.
Logwise ✓
UnknownAI-powered incident resolution for on-call teams