

Repository
aws-secrets-manager-k8s
Sync AWS Secrets Manager secrets into a Kubernetes cluster.
README
AWS Secrets Manager K8s

View all Roadmaps · Best Practices · Questions
Sync AWS Secrets Manager secrets into a Kubernetes
cluster.
Problem statement
While AWS Secrets Manager provides an API and various SDKs
to use it from within an application, it's either not possible or not wanted to modify any application to call AWS Secrets Manager directly.
The solution in this repository allows to sync secrets from AWS Secrets Manager into
Kubernetes Secrets to make them accessible
via as files or environment variables
for applications.
Implementation
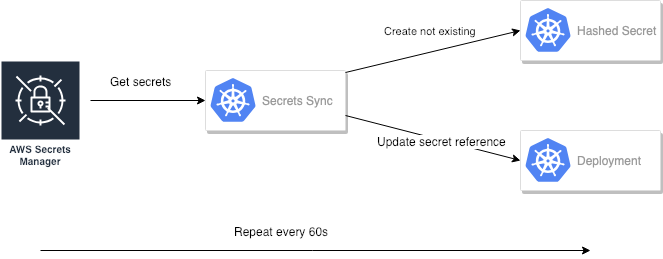
The CRD implements a continuous reconcile loop for every sync instance:
- List all secrets the AWS role can see
- Filter out not allowed prefixes and namespaces
- Convert them to hashed Kubernetes Secrets
- Create the hashed Kubernetes Secrets
- Update references to all managed secrets in
- Deployments
- StatefulSets
- CronJobs
- Sleep for one minute and restart
Usage
Create an AWS Role with access to the AWS Secrets Manager secrets you want to sync.
The secret names should have the following format: prefix/namespace/name, with the prefix
being an arbitrary string (e.g. production, staging) and namespace reflecting the targeted
Kubernetes Namespace and name of the to be created Kubernetes Secret.
Before defining the actual sync config, deploy the manager and CRD definition using make deploy into your cluster.
After that setup the actual sync similar to:
apiVersion: awssecretsmanager.nholuongut.net/v1alpha1
kind: Sync
metadata:
  labels:
    controller-tools.k8s.io: "1.0"
  name: sync-sample
spec:
  awsRoleARN: aws-role-to-be-used
  prefix: production/
  namespaces:
  - "default"
  - "monitoring"
Development
This project is developed using kubebuilder and follows the documented kubebuilder development workflow.
🚀 I'm are always open to your feedback. Please contact as bellow information:
[Contact ]
- [Name: Nho Luong]
- Skype
- Github
- Email Address
- PayPal.me

License
- Nho Luong (c). All Rights Reserved.🌟